
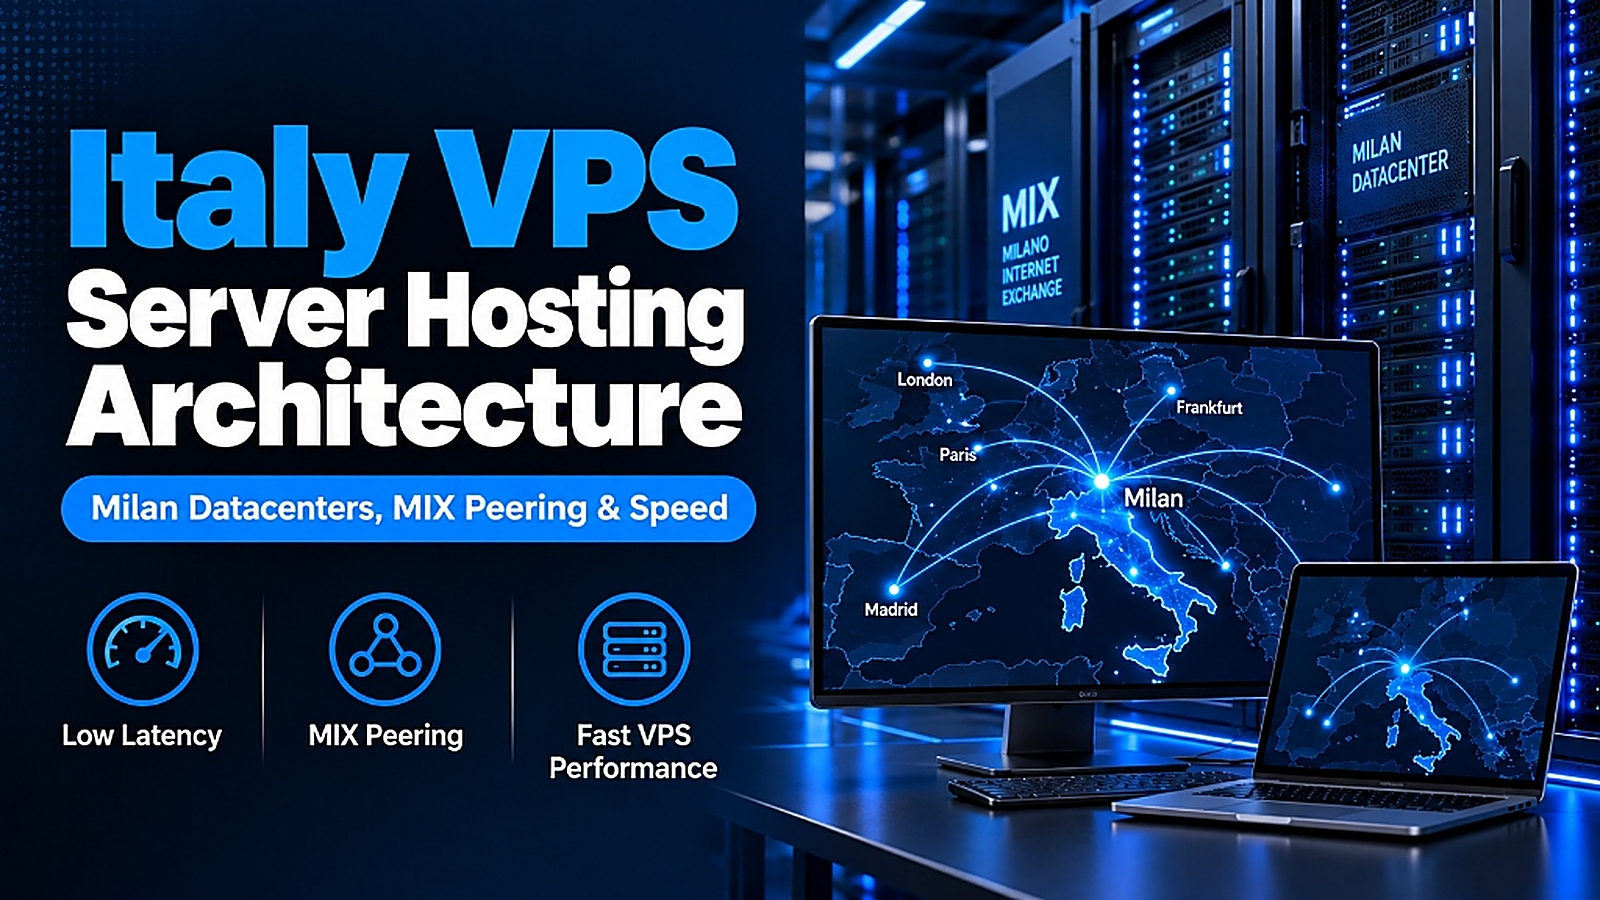
Deploying digital web infrastructure across Southern Europe requires establishing server presence at the heart of the Mediterranean digital crossroads. Italy serves as a critical telecommunications bridge connecting Southern Europe to North Africa, the Middle East, and Western Europe. Hosting within certified Tier-3 Milan datacenters provides sub-10ms round-trip latency across the Italian peninsula while ensuring strict data compliance under the European General Data Protection Regulation (GDPR) and local Garante oversight.
- Milan Internet Exchange (MIX) Peering and Southern European Transit: Direct optical cross-connects within Milan facilities provide single-hop packet transit across Italian broadband networks (TIM, Vodafone, Fastweb, Wind Tre).
- Hardware-Assisted KVM Virtualization and Dedicated ECC Compute: Deploying on Kernel-based Virtual Machine hypervisors guarantees dedicated CPU instruction execution and private physical memory blocks, shielding applications from neighboring tenant contention.
This technical architecture guide evaluates Italian transit mechanics, KVM hypervisor isolation, NVMe storage performance, and regulatory compliance for organizations deploying on an Italy VPS server solution.
Southern European Telecommunications Topology: The Strategic Power of Milan
Milan functions as Italy’s primary technological and financial capital, hosting the dense concentration of carrier-neutral datacenters across the Caldera business district. Datacenters in Milan are interconnected via high-capacity dark fiber rings with direct optical paths across the Alps into Frankfurt and Paris.
Hosting virtual private servers directly within Milan datacenters slashes domestic latency to between 1ms and 4ms across Lombardy, keeping response times under 10ms to Rome and Florence, and under 15ms to Naples and Sicily. For transactional platforms and latency-sensitive API backends, eliminating routing hops yields immediate improvements in Time-to-First-Byte (TTFB) and conversion metrics.
Furthermore, facilities connect directly with the Milan Internet Exchange (MIX), facilitating high-speed domestic peering between major Italian internet service providers and global content delivery networks.
Virtualization Architecture: KVM Hypervisor vs. Shared Containers
When selecting affordable virtual infrastructure, the underlying virtualization architecture governs application stability, security isolation, and hardware resource predictability. Legacy budget hosting providers often utilize container-based virtualization technologies like OpenVZ or LXC.
In containerized shared-kernel environments, all customer instances share the underlying host operating system’s single Linux kernel. A memory leak, runaway process, or kernel panic triggered on an adjacent tenant’s container can destabilize the entire physical node, crashing your web services unpredictably.
In contrast, modern cloud hosting utilizes Kernel-based Virtual Machine (KVM) technology. KVM operates as a true hardware-level Type-1 hypervisor embedded directly within the Linux kernel. Under KVM, each virtual server functions as an independent machine with its own virtualized BIOS, private kernel space, virtual PCIe controller, and dedicated memory addresses.
When evaluating VPS vs dedicated server upgrades, choosing KVM virtual machines provides systems engineers with total administrative sovereignty to tune kernel parameters, compile software packages, and implement advanced container runtimes without hypervisor restrictions.
For latency-critical SaaS and database backends, ensure your VPS utilizes Kernel-based Virtual Machine (KVM) virtualization with dedicated vCPU core affinity. This completely eliminates noisy-neighbor performance throttling.
Storage Array Performance: Direct-Attached NVMe RAID Arrays
Storage subsystem input/output throughput represents the primary physical constraint governing dynamic database queries and file retrieval. Legacy solid-state drives communicate through SATA controllers originally engineered for mechanical hard drives, limiting queue depth to thirty-two concurrent commands.
High-performance virtual instances utilize direct-attached enterprise Non-Volatile Memory Express (NVMe) solid-state storage organized in redundant RAID 10 configurations. Operating directly across high-speed PCIe Gen 4 lanes, NVMe drives support up to 64,000 parallel command queues.
To ensure high storage endurance and low disk write latency during heavy database inserts, administrators mount file systems using optimized mount parameters within /etc/fstab:
# Optimized NVMe storage mount options
UUID=be8a1f2b-9c3d-4e5f-8a1b-2c3d4e5f6a7b / ext4 noatime,nodiratime,commit=60,errors=remount-ro 0 1
Disabling access-time updates (noatime and nodiratime) eliminates unnecessary disk metadata writes whenever static files or cache assets are accessed, preserving physical storage bandwidth for core transactional database operations.
Out-of-Band Control Panels: Virtualizor Management
Reliable infrastructure management requires dependable out-of-band administration tools that function independently of the installed guest operating system. If an administrator accidentally introduces a restrictive firewall rule or encounters a kernel panic during an upgrade, standard SSH access terminates immediately.
Enterprise virtual hosting environments incorporate intuitive web-based virtualization management control panels, including the Virtualizor cloud management control panel. This out-of-band management framework connects directly to the underlying KVM hypervisor daemon via encrypted VNC and HTML5 Serial Console interfaces.
Administrators can execute cold server reboots, mount recovery ISO images, view real-time resource utilization graphs, and perform automated snapshot backups from an intuitive graphical dashboard. Having out-of-band console access eliminates emergency technician dispatch delays and guarantees administrative recovery regardless of software state.
Enterprise cloud instances provisioned on pure NVMe arrays deliver over 500,000 read/write IOPS, ensuring sub-millisecond database query response times even during extreme unpredicted traffic surges.
Linux Network Kernel Optimization: Google BBR and Socket Scaling
Default Linux kernel networking parameters are engineered for conservative local network environments rather than high-throughput public cloud infrastructure. Tuning TCP socket buffers and congestion control algorithms allows your virtual server to handle thousands of concurrent client connections without packet drops.
1. Activating Google BBR Congestion Control
Standard Linux networking stacks employ older loss-based congestion control algorithms like Cubic. On public internet transit routes, random packet loss causes Cubic to slash transmission throughput prematurely.
Google’s BBR (Bottleneck Bandwidth and Round-trip propagation time) algorithm models physical network path capacity directly, maximizing throughput while minimizing queueing latency:
# Enable Google BBR TCP congestion control (/etc/sysctl.conf)
net.core.default_qdisc = fq
net.ipv4.tcp_congestion_control = bbr
2. Expanding System Connection Queues
Scaling kernel network buffers allows the server to accommodate massive data transfers and high concurrent socket connections without dropping incoming TCP handshakes:
# Network socket buffer scaling
net.core.somaxconn = 65535
net.core.netdev_max_backlog = 100000
net.ipv4.tcp_max_syn_backlog = 3240000
net.ipv4.tcp_rmem = 4096 87380 16777216
net.ipv4.tcp_wmem = 4096 65536 16777216
Applying these values with sysctl -p ensures that heavy inbound marketing campaigns or seasonal eCommerce traffic surges never saturate socket connection queues at the operating system layer.
In-Memory Caching & Database Tuning: MariaDB Buffer Pools & Redis
High-concurrency web applications place heavy transactional demands on relational databases. Default database configurations often exhaust thread allocations during unexpected visitor spikes, stalling active web workers.
Allocating up to seventy percent of server memory to the MariaDB InnoDB buffer pool ensures that frequently requested catalog tables, pricing rules, and user sessions remain cached in volatile RAM, minimizing physical disk reads.
Implementing persistent connection pooling with ProxySQL or deploying a localized Redis in-memory cache offloads repetitive database queries, returning cached responses in sub-millisecond timeframes.
Zero-Trust Perimeter Security: UFW, Nftables and WireGuard Endpoints
Exposing virtual servers directly to the public internet requires establishing a disciplined zero-trust network perimeter. Enterprise systems administrators implement strict packet filtering policies using modern Linux Nftables or Uncomplicated Firewall (UFW).
Default firewall rules block all unsolicited inbound traffic across non-essential ports, restricting public internet access strictly to encrypted web traffic on ports 80 and 443.
Remote administrative interfaces—including SSH, Virtualizor management daemons, and internal database ports—are isolated behind encrypted WireGuard VPN tunnels. Enforcing multi-factor public key authentication completely neutralizes automated credential brute-force attacks and port scanning vulnerabilities.
Automated System Telemetry: Node Exporter and CPU Frequency Governors
Modern enterprise server processors feature dynamic power-saving governors that throttle execution frequencies during periods of low activity. However, in transactional database environments, the brief latency penalty incurred when stepping up clock frequencies can introduce perceptible request jitter.
Systems engineers configure Linux CPU frequency scaling governors to maximum performance mode (performance). Locking processor cores to their maximum base clock frequency eliminates frequency-scaling latency spikes, guaranteeing deterministic execution times for real-time web requests.
Additionally, disabling processor C-states in system BIOS settings prevents server cores from dropping into deep sleep states, maintaining immediate CPU readiness for high-concurrency microservice workloads.
To further reduce connection handshake overhead for returning visitors, systems engineers enable TCP Fast Open (net.ipv4.tcp_fastopen = 3). TCP Fast Open allows data exchange during the initial SYN packet handshake, eliminating an entire network round-trip time (RTT) for repeat client connections.
Combining TCP Fast Open with modern HTTP/3 (QUIC) protocols on Italy virtual servers delivers near-instantaneous page rendering speeds across broadband networks throughout Southern Europe, minimizing initial connection lag for repeat visitors across the Italian peninsula.
Require High-Availability VPS Infrastructure with Guaranteed Uptime?
Deploy enterprise-grade KVM virtual servers backed by pure NVMe storage arrays, automated out-of-band management, and 24/7 technical monitoring.
Frequently Asked Questions
Q1
Why is Milan the premier datacenter location for Italian hosting?
+
Milan hosts the Milan Internet Exchange (MIX) and represents Italy’s financial and economic heart. Hosting in Milan delivers sub-10ms latency across northern and central Italy and sub-15ms to southern Italy, with direct high-speed optical routes into Central Europe.
Q2
What specific kernel parameters are recommended for Italy VPS Server Hosting Architecture?
+
Tuning vm.swappiness to 10, increasing fs.file-max beyond 2,000,000, and expanding net.core.somaxconn to 65535 optimizes high-concurrency request handling on Italy VPS Server Hosting Architecture.
Q3
What storage redundancy options are available on an Italy VPS?
+
Virtual instances deploy direct-attached enterprise NVMe solid-state drives configured in RAID 10 arrays. This architecture delivers millions of random IOPS while protecting against physical drive failures without downtime.
Q4
How does Italy VPS Server Hosting Architecture isolate tenant memory from noisy-neighbor interference?
+
KVM hardware virtualization enforces dedicated guest memory spaces with memory ballooning disabled, guaranteeing that allocated RAM remains strictly reserved for your applications.
Q5
Can I configure automated snapshot backups on an Italy VPS?
+
Yes. Virtualizor supports scheduled block-level snapshot backups and automated offsite replication to secondary cloud vaults, ensuring rapid point-in-time disaster recovery during critical incidents.
