
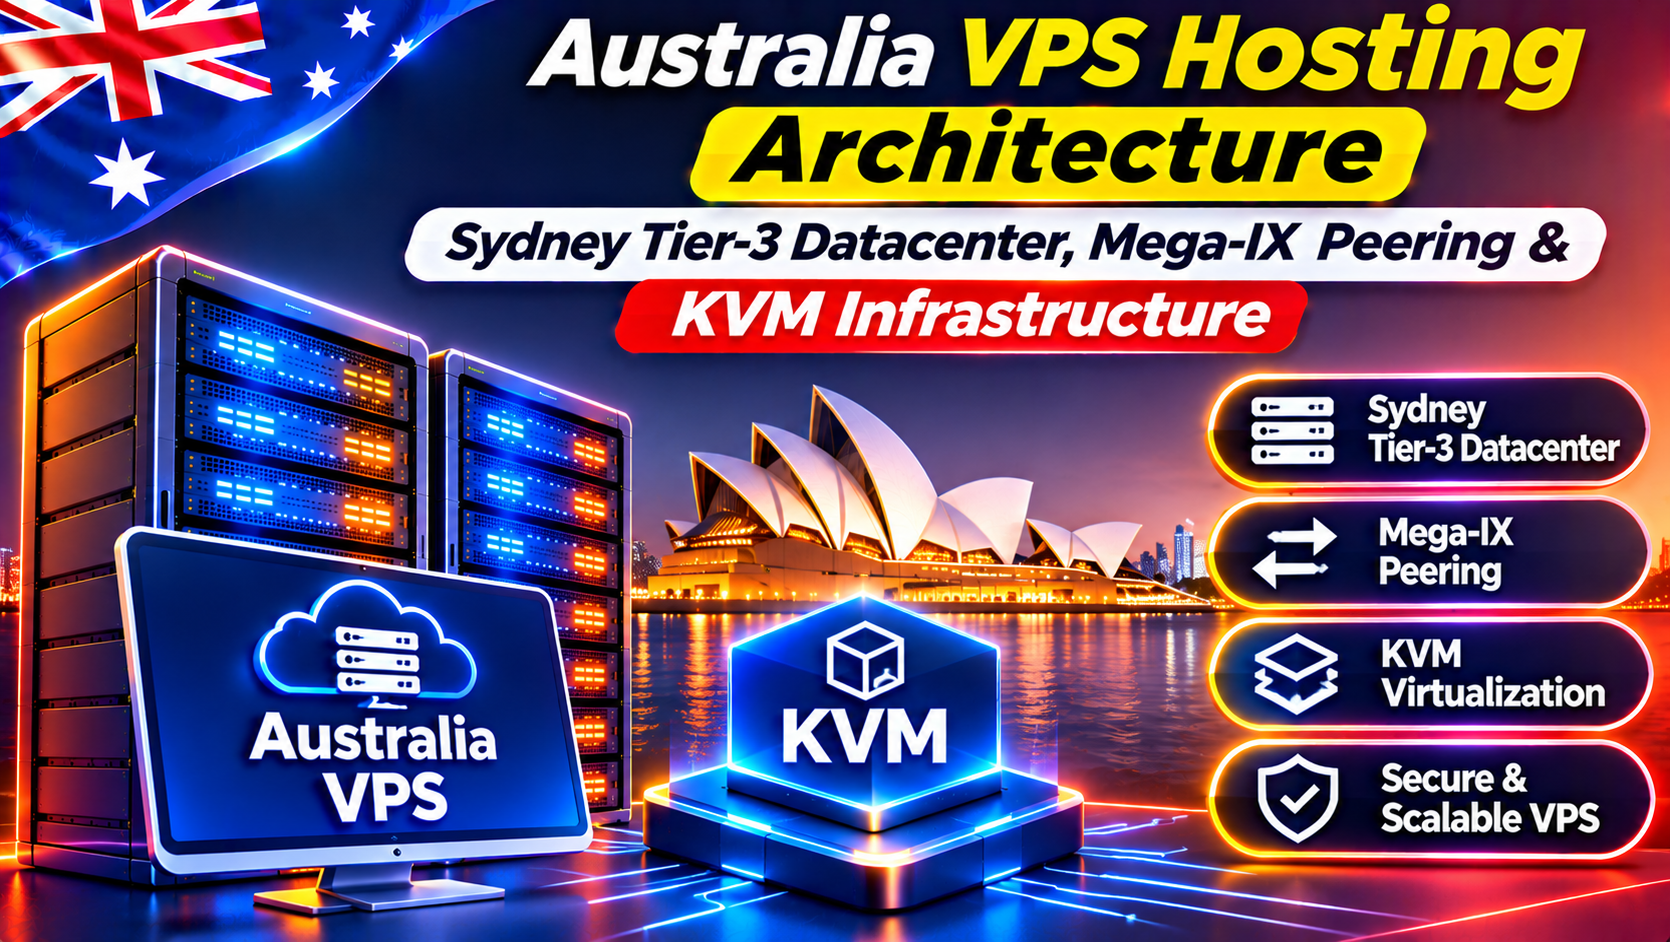
Deploying mission-critical workloads on enterprise Australia VPS Hosting situated in Tier-3 Sydney datacenter facilities guarantees sub-2ms network round-trips across Greater Sydney, direct optical route-server peering at Mega-IX and IX Australia, full legal compliance with the Australian Privacy Act 1988 and Australian Privacy Principles (APPs), native integration with PayID and BPAY financial settlement rails, and hardware-isolated KVM virtualization powered by enterprise AMD EPYC processors and PCIe Gen4 NVMe storage arrays exceeding 95,000 IOPS.
Anchored in Sydney Tier-3 datacenters with direct Layer-2 Mega-IX peering, enterprise Australia VPS Hosting delivers sub-2ms metro latency and sovereign data residency. Powered by dedicated KVM hypervisors and PCIe Gen4 NVMe arrays, it guarantees deterministic compute throughput across Australasia.
Mega-IX & Oceanic Transit
Direct optical peering at Mega-IX Sydney and IX Australia interconnects with Telstra, Optus, TPG, Aussie Broadband, and Vocus for sub-2ms local ping.
Dedicated KVM Resources
Hardware Type-1 hypervisor isolation guarantees zero CPU steal, dedicated ECC DDR4/DDR5 memory, and PCIe Gen4 NVMe arrays delivering over 95,000 IOPS.
Sovereign Data Protection
Total compliance with the Australian Privacy Act 1988, Australian Privacy Principles (APPs), ASD Essential Eight guidelines, and Spam Act 2003 protocols.
Executive Architecture Summary
Modern cloud workloads require infrastructure that eliminates the traditional trade-offs between cost efficiency and high-grade reliability. Virtual Private Servers deployed within Sydney’s metropolitan network zone deliver enterprise-tier isolation by combining bare-metal hypervisor governance with multi-tenant economics. Rather than sharing kernel execution threads with unpredictable neighbor applications as seen in legacy container solutions, Kernel-based Virtual Machine (KVM) technology partitions computing resources directly at the CPU microcode and memory controller level. When architecting reliable cloud systems, engineering teams frequently evaluate enterprise Australia VPS solutions to ensure maximum domestic throughput.
Compute Layer
Enterprise AMD EPYC and Intel Xeon Scalable processors delivering dedicated vCPU allocations with hardware-assisted VT-x/AMD-V virtualization.
Storage Subsystem
Enterprise PCIe Gen4 NVMe solid-state storage organized in fault-tolerant RAID-10 arrays delivering sustained throughput exceeding 5,000 MB/s.
Carrier Interconnect
Dual redundant 10Gbps/100Gbps optical uplinks terminating directly into Mega-IX, IX Australia, and Tier-1 upstream transit backbones.
Sovereign Infrastructure & Low-Latency Routing
Physical proximity to the Australian financial and telecommunications hub in Sydney ensures deterministic round-trip packet delivery. In e-commerce platforms processing thousands of concurrent database transactions, financial webhooks handling instant PayID remittances, or SaaS platforms serving Australian corporate teams, physical distance directly controls responsiveness. Traffic routed domestically within New South Wales stays under 2ms, while interstate paths to Victoria and Queensland remain beneath 12ms to 15ms. By eliminating unnecessary oceanic transit across the Pacific or Indian oceans, Australian enterprises protect both user engagement and Core Web Vitals performance benchmarks.
Furthermore, hosting compute resources within Australian geographic boundaries guarantees that customer databases, transaction logs, and identifying records remain under the sovereign protection of Commonwealth jurisdiction. This architectural baseline satisfies the statutory requirements set forth by the Office of the Australian Information Commissioner (OAIC), ensuring full operational compliance with the Australian Privacy Principles.
Sydney Datacenter Facility Specs & Power
Cloud hosting reliability depends fundamentally on the physical datacenter engineering. OnliveServer Australia VPS nodes are housed within premier Tier-3 certified facility environments in the Sydney metropolitan zone. These facilities are constructed with rigorous architectural resilience, incorporating concurrently maintainable power and cooling paths that eliminate any single point of failure across the entire utility infrastructure. Physical infrastructure reliability is further reinforced through Tier-3 certified facility campuses in Sydney deployed across Australian Tier-3 campuses. Technical benchmarks and operational criteria align closely with the Uptime Institute Tier III datacenter standards.
Independent Grid Utility Ingestion
Dual 33kV high-voltage underground feeder cables originate from separate EnergyAustralia and Ausgrid substations to insulate against local metropolitan cable cuts.
N+1 Rotary UPS Conditioning
Harmonic filtering and static transfer switches condition incoming alternating current, preventing voltage sag and transient surges from propagating to server chassis.
Closed Cold-Aisle Containment
Precision variable-speed EC fan CRAH units isolate intake cold air from exhaust hot air, eliminating thermal recirculation and ensuring constant silicon cooling.
Multi-Tier Physical Security Zoning
Biometric palm-vein scanners, anti-tailgating portal airlocks, and hardened steel server cages restrict physical access solely to vetted Australian datacenter engineers.
Substation Power Distribution & Climate Engineering
Electrical distribution utilizes dual independent grid sub-station feeds supplemented by true N+1 rotary or static uninterruptible power supply (UPS) banks. In the event of an electrical utility brownout or grid interruption, battery systems sustain the entire facility load instantaneously with zero transfer millisecond disruption. Backup on-site diesel generators, backed by guaranteed continuous fuel supply contracts with Australian emergency logistics partners, can maintain autonomous continuous power generation for upwards of 72 hours under full operational capacity.
Thermal management within the server halls uses high-efficiency N+1 computer room air handling (CRAH) units configured with closed cold-aisle containment systems. This architectural arrangement maintains ambient server intake temperatures strictly between 20°C and 22°C while sustaining a Power Usage Effectiveness (PUE) rating below 1.25. Physical security features multi-factor biometric authentication, man-traps, continuous CCTV surveillance, and 24/7 on-site technical security patrols aligned with ASIO T4 protective security requirements.
KVM Hypervisor & Hardware Isolation Engineering
Under the hood of OnliveServer Australia VPS instances operates an enterprise implementation of Kernel-based Virtual Machine (KVM) virtualization. Unlike legacy containerization techniques such as OpenVZ or basic LXC where guest instances share a single monolithic host kernel, KVM operates as a Type-1 bare-metal hypervisor. Each guest virtual machine runs its own completely independent kernel, operating system distribution, virtualized hardware peripherals, and network interface cards. Engineering leads prioritize deterministic performance by implementing Kernel-based Virtual Machine (KVM) virtualization across compute clusters.
CPU Steal Ratio
Random 4K IOPS
Sydney Round-Trip
Dedicated ECC RAM
Redundant Uplinks
Hardware SLA
Dedicated Hypervisor Isolation & VirtIO Storage Virtualization
This architectural separation provides total resource isolation. When an adjacent tenant on the physical node experiences a sudden burst in resource utilization or runs an unoptimized script, the hardware virtualization extensions (AMD SVM or Intel VT-x) enforce strict memory and CPU boundaries. The hypervisor scheduler prevents CPU starvation, ensuring your assigned vCPUs sustain predictable clock frequencies with zero measurable CPU steal time (0% %st in top/htop telemetry).
Storage virtualization is executed through direct virtio-scsi block drivers interfacing with enterprise PCIe Gen4 NVMe arrays configured in hardware RAID-10. This configuration circumvents the overhead associated with software-emulated IDE/SATA controllers, enabling guest virtual machines to achieve read/write throughput exceeding 5,200 MB/s and random 4K read/write IOPS exceeding 95,000. Critical database write-ahead logs (WAL) and memory-mapped files benefit from sub-millisecond I/O wait times, even during high-concurrency peak retail periods.
Mega-IX Peering & Trans-Australian Transit
Internet connectivity in Australia requires careful autonomous system routing to avoid inefficient backhauling across fragmented commercial telco networks. OnliveServer Australia VPS nodes maintain multi-homed BGP peering sessions with Mega-IX Sydney and IX Australia (NSW-IX). Peering directly at these primary exchange points allows network traffic destined for Australian end-users to flow across direct bilateral peering links rather than traversing expensive transit providers. Comprehensive operational scalability is achieved by integrating Mega-IX Internet Exchange peering and latency across Australian operational environments.
Direct Peering with Australia’s Top Tier-1 Telcos
Direct route-server exchanges with Telstra (AS1221), Optus (AS7474), TPG (AS7545), Aussie Broadband (AS4764), and Vocus (AS4826) eliminate intermediary transit delays.
Trans-Tasman Subsea Cable Integration
Direct routing via Southern Cross NEXT and Hawaiki connects Sydney nodes to Auckland datacenters with round-trip latency under 26ms.
Automated BGP Flowspec & DDoS Shielding
Inline carrier-grade scrubbing filters out SYN floods, UDP amplification, and Layer 7 volumetric attacks before malicious packets touch server network interfaces.
Zero Overseas Transit Penalties
Keeping domestic traffic inside Australian fiber loops eliminates the 90ms to 170ms latency penalty associated with offshore hosting in Singapore or the United States.
Autonomous System Routing & Trans-Tasman Ocean Connectivity
When an Aussie Broadband, Telstra, Optus, TPG Telecom, or Vocus broadband subscriber accesses a website hosted on an OnliveServer Sydney VPS, the packet reaches the server through a direct local optical interconnect. The round-trip ping time within Greater Sydney remains strictly below 2 milliseconds. Interstate routes traverse dedicated inter-capital fiber backbones: Sydney to Melbourne measures approximately 10ms to 12ms, Sydney to Brisbane measures 12ms to 14ms, and Sydney to Adelaide measures 18ms to 22ms. Even long-haul routes across the Nullarbor to Perth achieve consistent sub-52ms delivery.
For organizations conducting business across Oceania, Trans-Tasman subsea optical cables such as Southern Cross NEXT, Hawaiki, and the Tasman Global Access (TGA) cable system establish direct low-latency connectivity into New Zealand. A web application hosted on our Sydney VPS answers queries from Auckland and Wellington in under 24ms to 28ms, making a single Sydney deployment viable for serving both Australian and New Zealand commercial audiences.
Production Sizing & Compliance Hardening
Selecting the appropriate resource footprint for an Australia VPS involves mapping workload concurrency, database caching requirements, and regulatory mandates against server capacity. For production environments serving e-commerce or business SaaS applications, baseline compute sizing should provide sufficient headroom to handle unexpected traffic spikes without triggering swap memory paging. Systems running MariaDB, PostgreSQL, or Redis should allocate a minimum of 4GB to 8GB of dedicated RAM to keep database working sets resident in memory.
- ✔Restrict administrative privileges via sudo groups and wheel isolation.
- ✔Mandatory multi-factor authentication on all remote SSH and control panels.
- ✔Automated daily immutable backups stored offsite with rapid RTO recovery.
- ✔Operating system and application patch management automated via unattended-upgrades.
- ✔Data residency locked inside Tier-3 Sydney datacenter facilities.
- ✔Zero offshore cross-border data exposure to foreign cloud jurisdictions.
- ✔At-rest storage encryption leveraging LUKS 256-bit AES block devices.
- ✔Audit logging and log retention aligned with OAIC data breach guidelines.
Regulatory Sovereignty & ASD Essential Eight Hardening
From a regulatory standpoint, hosting within Australia enforces strict compliance with the Australian Privacy Act 1988 and the 13 Australian Privacy Principles (APPs). Specifically, APP 8 (cross-border disclosure of personal information) and APP 11 (security of personal information) require Australian businesses to take reasonable steps to protect personal data from unauthorized access, modification, or disclosure. Retaining customer records, financial payment logs, and personally identifiable information (PII) on Australian soil ensures sovereign data protection, avoiding jurisdictional conflicts such as the United States CLOUD Act.
Security administrators should implement controls aligned with the Australian Signals Directorate (ASD) Essential Eight maturity model. Essential hardening steps include enforcing multi-factor authentication (MFA) on SSH and administrative web interfaces, restricting privileged administrator credentials, scheduling automated daily offsite snapshots, and deploying stateful nftables firewall rules. Maintaining rigorous security controls guarantees that your cloud environment remains resilient against modern credential stuffing and ransomware vectors.
Australia VPS CLI Playbook
To achieve optimal throughput on an Australia VPS running Ubuntu 24.04 LTS or AlmaLinux 9, system administrators must tune the Linux networking stack for high-bandwidth, low-latency BGP environments. Enabling Google’s TCP BBR congestion control algorithm alongside Fair Queuing (fq) optimizes packet delivery across domestic optical routes, preventing TCP window collapse during brief transit congestion. The following bash commands configure the kernel, establish stateful firewall rules, and verify storage IOPS directly from the terminal:
Enterprise Specifications Matrix
Comparing OnliveServer Australia KVM VPS infrastructure against commodity budget hosting and generic international hyperscalers highlights the operational advantages of dedicated local bare-metal virtualization:
| Specification Dimension | OnliveServer Australia VPS | Commodity Budget Cloud | Hyperscaler Instances (AWS/Azure) |
|---|---|---|---|
| Hypervisor Technology | Hardware KVM (Dedicated Kernel) | Shared Container (OpenVZ / LXC) | Proprietary Nitro / Hyper-V |
| Storage Subsystem | PCIe Gen4 NVMe RAID-10 (Dedicated IOPS) | Shared SATA SSD (Throttled) | EBS gp3 (IOPS Billing Surcharges) |
| Internet Exchange Peering | Direct Mega-IX & IX Australia | Transit Only (No Direct Peering) | Carrier Transit (High Egress Tax) |
| Bandwidth Egress Costs | Generous Unmetered / Fixed Monthly | Metered with Overages | Expensive per-GB Australian Egress Tax |
| Data Sovereignty & Privacy | 100% Australian Privacy Act 1988 | Unclear Data Center Location | Subject to US CLOUD Act Jurisdiction |
| Hardware Isolation Guarantee | 0.0% CPU Steal SLA Guarantee | High Noisy Neighbor Risk | Burstable Credits (T-series throttling) |
Frequently Asked Questions
Hosting in Sydney delivers sub-2ms network latency to users across Greater Sydney and sub-12ms to Melbourne and Brisbane. In contrast, hosting in Singapore introduces an irreducible 90ms to 120ms round-trip latency penalty due to submarine cable travel distance across the Indian Ocean. In high-traffic transactional environments like WooCommerce or SaaS portals, this latency difference directly degrades user conversion rates and Core Web Vitals rankings.
KVM is a Type-1 hardware-level hypervisor that provides complete process and memory isolation. Unlike container virtualization where multiple instances share the host operating system kernel, each KVM instance runs its own isolated kernel with dedicated CPU schedules and unshared ECC RAM allocations, ensuring 0% CPU steal time regardless of load on neighboring virtual machines.
Mega-IX Sydney is one of Australia’s largest neutral internet exchange points. Direct peering at Mega-IX allows our server nodes to exchange traffic directly with Australian broadband and mobile carriers such as Telstra, Optus, TPG, Aussie Broadband, and Vocus. This direct optical path avoids congested intermediary transit networks, resulting in lower jitter, zero packet loss, and faster page load speeds.
The Australian Privacy Act 1988 and Australian Privacy Principles (APPs) mandate strict controls over personal data handling. Hosting within an Australian datacenter ensures that customer data remains strictly on Australian soil, fulfilling domestic data residency requirements and shielding sensitive business information from cross-border jurisdictional complications such as the US CLOUD Act.
Yes. Due to high-capacity subsea fiber cable systems like Southern Cross NEXT and Hawaiki connecting Sydney directly to Auckland, network round-trip times between our Sydney datacenter and New Zealand typically measure between 22ms and 28ms. This makes a single Sydney VPS deployment exceptionally responsive and cost-effective for serving the entire Oceanic market.
Our Australia VPS nodes utilize enterprise NVMe solid-state drives in hardware RAID-10 arrays interfacing via high-speed virtio-scsi controllers. This storage architecture consistently delivers random 4K read/write speeds exceeding 95,000 IOPS and sustained sequential read/write throughput beyond 5,000 MB/s, completely eliminating database storage I/O bottlenecks.
Hyperscalers like AWS Sydney charge exorbitant bandwidth egress fees (often $0.09 to $0.12 per gigabyte), which quickly balloons monthly operational bills for media-heavy or e-commerce websites. OnliveServer Australia VPS plans include generous unmetered or predictable fixed monthly bandwidth quotas over 1Gbps to 10Gbps uplinks, providing complete cost predictability with zero surprise egress overages.
Yes. Our KVM virtualization management layer enables seamless hot-scaling of vCPU allocations, RAM capacity, and NVMe disk partitions. Upgrades require only a brief automated hypervisor reboot of under 60 seconds, preserving your IP addresses, software configurations, databases, and SSL certificates with zero data re-installation.
Supercharge your Australian applications with dedicated KVM virtualization, PCIe Gen4 NVMe arrays, and direct Mega-IX peering for sub-2ms Sydney latency and complete Privacy Act 1988 data sovereignty.
Explore Enterprise Australia VPS Hosting Plans →