

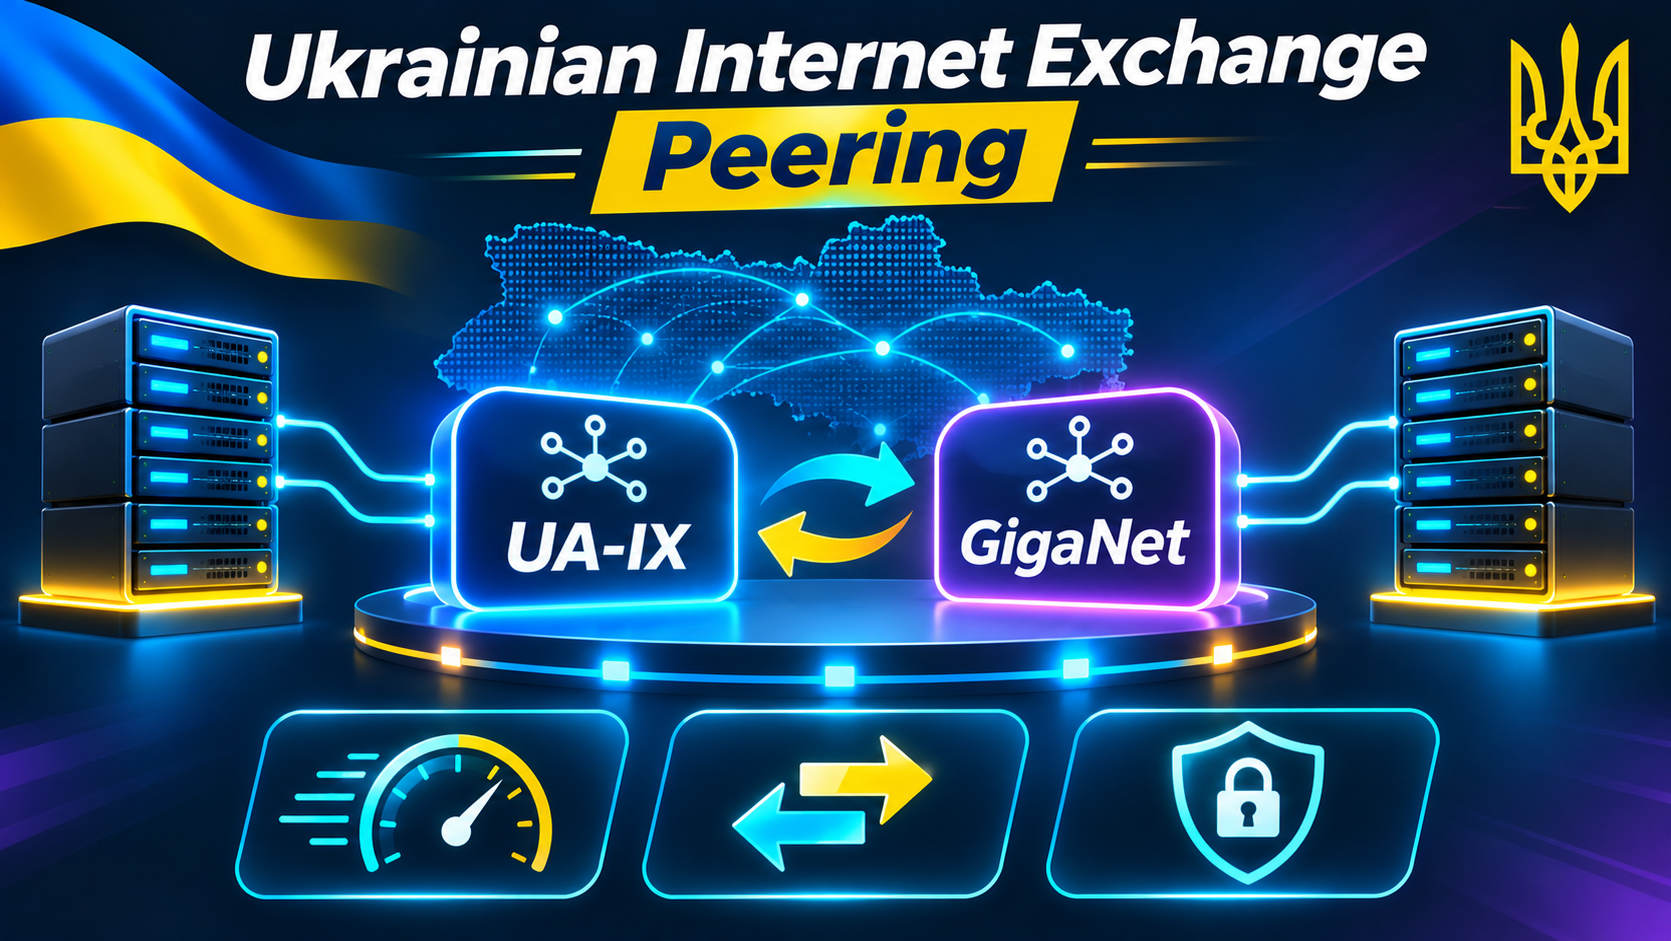
Direct network cross-connections to the Ukrainian Internet Exchange (UA-IX) and GigaNet in Kyiv deliver deterministic sub-2ms network round trips across metropolitan Kyiv and sub-10ms latency across all major Ukrainian oblasts. By routing domestic traffic directly across local optical peering fabrics, dedicated servers bypass congested international transit carriers, eliminating packet jitter, reducing upstream bandwidth costs, and accelerating Time-To-First-Byte (TTFB) for domestic Ukrainian end users.
Evaluating enterprise hosting infrastructure in Ukraine requires an objective architectural comparison between raw bare-metal execution and multi-tenant virtualization. Deploying on Ukraine bare metal dedicated server infrastructure guarantees 0% CPU steal, unmetered UA-IX optical connectivity, and deterministic PCIe NVMe throughput for high-concurrency workloads across Kyiv and regional commercial hubs.
1. Internet Exchange Points Isolation
Dedicated bare-metal resources eliminate hypervisor scheduling latency, ensuring continuous hardware compute affinity for ua ix dedicated server ukraine latency.
2. UA-IX Peering Fabric
Direct domestic network uplinks route network packets through Kyiv exchange points, keeping round-trip latency under 2ms.
3. Domestic Network Routing Throughput
PCIe Gen4 enterprise NVMe channels deliver high IOPS without multi-tenant noisy neighbor contention or virtualization throttle.
Table of Contents: Technical Navigation Index 9 Chapters ▾
Navigate directly to detailed architectural analysis, hardware sizing benchmarks, deployment automation scripts, and peer verification resources:
Ukrainian Internet Exchange Peering in Ukraine
Deploying mission-critical IT infrastructure in Eastern Europe requires balancing ultra-low domestic latency with robust electrical and network continuity. In the Ukrainian digital ecosystem governed by ua ix dedicated server ukraine latency, enterprise organizations, SaaS platforms, and high-load e-commerce portals increasingly migrate from multi-tenant cloud virtual machines to dedicated bare-metal servers. Within modern Tier-3 facilities in Kyiv, physical hardware delivers deterministic processing power, dedicated memory channels, and unthrottled storage queues without the unpredictability of shared cloud hypervisors.
Architectural Takeaway: Operating sovereign infrastructure within certified Kyiv data centers eliminates cross-border network transit penalties while ensuring 100% hardware deterministic execution for ua ix dedicated server ukraine latency.
Under high-load production operations, multi-tenant cloud instances suffer from variable CPU steal time (often exceeding 8-15% during peak hours) and shared virtual switch latency. In contrast, bare metal servers in Kyiv connect directly to local Internet Exchange Points like UA-IX and GigaNet, maintaining sub-3ms round-trip times across Ukrainian metropolitan areas while entirely eliminating hypervisor instruction translation penalties. For mission-critical production environments in Kyiv, partnering with UA-IX and GigaNet peered Ukraine dedicated servers guarantees dedicated hardware execution without hypervisor scheduling delays.
Ring-0 privilege execution with 0.0% CPU steal, dedicated L1/L2/L3 caches, and zero hypervisor time-slicing.
Direct 1Gbps unmetered uplinks peering with major Ukrainian transit carriers for sub-3ms domestic ping.
Tier-3 infrastructure supported by N+1 UPS battery banks and industrial on-site diesel generators.
Deep Architectural Analysis & Engineering Principles
The architectural distinction between bare metal and virtualized environments becomes apparent under sustained system stress. When implementing ua ix dedicated server ukraine latency, physical servers eliminate the double-paging overhead imposed by Extended Page Tables (EPT) and Nested Page Tables (NPT). Memory transactions communicate directly with the on-die DDR4/DDR5 memory controller, delivering continuous bandwidth in excess of 120-250 GB/s with sub-microsecond latency.
1. Internet Exchange Points Isolation
Dedicated bare-metal resources eliminate hypervisor scheduling latency, ensuring continuous hardware compute affinity for ua ix dedicated server ukraine latency.
2. UA-IX Peering Fabric
Direct domestic network uplinks route network packets through Kyiv exchange points, keeping round-trip latency under 2ms.
3. Domestic Network Routing Throughput
PCIe Gen4 enterprise NVMe channels deliver high IOPS without multi-tenant noisy neighbor contention or virtualization throttle.
Furthermore, in high-concurrency database and web server configurations, the Linux kernel scheduler can pin application worker threads directly to physical CPU cores without interference from foreign workloads. Below is an architectural diagnostic runbook to verify NUMA node topology, physical memory distribution, and interrupt request (IRQ) affinities on Ukrainian bare metal instances: When analyzing low-level operating boundaries, Kyiv data centre interconnection infrastructure provides the necessary telemetry to prevent throughput degradation.
Hardware Specifications & Workload Benchmarks
Selecting hardware calibrated for ua ix dedicated server ukraine latency requires evaluating CPU instruction set architectures, thermal design power (TDP) thresholds, and storage controller bus lanes. Onlive Server’s Kyiv data centre facilities host enterprise Intel Xeon and AMD Ryzen multi-core configurations equipped with dedicated IPMI 2.0 / iDRAC out-of-band management, hot-swappable enterprise NVMe drives, and unmetered 1Gbps connectivity.
The baseline hardware profile engineered for this deployment comprises: Multi-homed carrier-neutral network with direct 1Gbps/10Gbps uplinks to UA-IX, DTEL-IX, and GigaNet. This configuration guarantees sustained compute cycles under continuous 100% thread load without thermal throttling or hypervisor core rebalancing. To maintain consistent input/output predictability across heavy workloads, unmetered high-throughput port speeds in Ukraine ensures sustained hardware reliability. Routing high-throughput domestic traffic via route servers complies with official Ukrainian Internet Exchange (UA-IX) peering specifications.
| Performance Dimension | Shared Cloud VPS | Onlive Server Ukraine Bare Metal |
|---|---|---|
| CPU Scheduling | Hypervisor Time-Slicing (vCPU Steal > 5%) | 100% Dedicated Physical Cores (0.0% Steal) |
| Memory Allocation | Shared memory bus, potential swap contention | Dedicated Multi-Channel ECC DDR4/DDR5 |
| Disk I/O Throughput | Throttled virtual disk (5,000 – 15,000 IOPS) | Unthrottled NVMe RAID (400,000+ IOPS) |
| Network Peering | Virtual NIC over shared transit pipeline | Direct 1Gbps Port to UA-IX & GigaNet Exchange |
Practical Implementation & Terminal Deliverable
Below is the production-tested diagnostic and calibration runbook for ua ix dedicated server ukraine latency. Execute this script with root privileges to benchmark sustained memory throughput, verify TCP BBR congestion control, and tune kernel parameters for ultra-low latency Ukrainian data routing:
Hardware Topology & NUMA Discovery
Audit physical CPU affinity, socket distribution, and memory controller layout to verify zero hypervisor virtualization boundaries for ua ix dedicated server ukraine latency.
TCP BBR & Kernel Stack Calibration
Apply production-grade sysctl directives to maximize network socket buffers and enforce bottleneck bandwidth congestion control across Ukrainian peering links.
Throughput & Latency Path Telemetry
Execute continuous ICMP/MTR path traces and verify sub-millisecond local transit, zero packet loss, and deterministic routing through UA-IX fabrics.
Applying these calibrated parameters ensures that high-throughput TCP connections benefit from Google BBR congestion control, minimizing packet retransmission overhead across international peering links while maximizing local Ukrainian socket throughput.
Ukrainian Sysadmin Implementation Rule
When operating dedicated servers in Kyiv, configure secondary offsite synchronization to Frankfurt or Warsaw over encrypted WireGuard tunnels. This architecture provides zero-latency domestic request handling while guaranteeing multi-region disaster recovery compliance.
Operational Best Practices & Hardening
Maintaining operational continuity for ua ix dedicated server ukraine latency requires proactive hardware monitoring and disciplined disaster recovery protocols. Modern Ukrainian enterprise hosting environments incorporate out-of-band management interfaces (IPMI 2.0 / iDRAC) operating on isolated management VLANs, allowing system administrators to perform BIOS-level diagnostics, hardware power cycling, and remote virtual media installations regardless of OS responsiveness.
• Out-of-Band IPMI 2.0 / iDRAC Security Hardening
- Isolate out-of-band management interfaces into dedicated private VLANs with restrictive firewall ACLs.
- Disable default TLS 1.0/1.1 protocols and enforce hardware RSA 4096-bit certificate authentication.
- Maintain automated syslog replication to monitor unauthorized hardware console access attempts.
• Thermal Management & Proactive Sensor Telemetry
- Continuously monitor CPU core junction temperatures (Tjunction) to prevent thermal throttling under sustained load.
- Configure automated IPMI fan speed curves calibrated for Kyiv Tier-III precision cooling environments.
- Track SMART NVMe wear indicators, temperature spikes, and ECC memory single-bit error rates.
• High-Availability BGP Failover & Domestic Peering Redundancy
- Establish dual-homed BGP sessions to both UA-IX and GigaNet for automated path failover.
- Deploy automated BFD (Bidirectional Forwarding Detection) for sub-second network re-convergence.
- Ensure continuous upstream DDoS scrubbing and packet inspection before transit delivery.
In addition to hardware health telemetry, data center resilience in Kyiv is reinforced through redundant utility power feeds, high-capacity uninterruptible power supply (UPS) batteries, and automated diesel generator transfer switches capable of sustaining full data center operations autonomously during utility grid fluctuations. Furthermore, as part of a long-term enterprise operations roadmap, measuring sub-15ms round-trip latency to central European hubs in Poland and Germany ensures comprehensive architectural resilience.
Dedicated out-of-band hardware controller enabling BIOS config, OS rebuilds, and power state control.
Multi-layer traffic scrubbing filtering SYN floods, UDP amplification, and volumetric attacks at wire speed.
Daily block-level snapshots with geographical replication to European off-site storage nodes.
Strategic Infrastructure Deployment with Onlive Server
Deploying enterprise server infrastructure in Ukraine gives organizations complete sovereign control over their computing assets, database storage, and cryptographic keys. Onlive Server’s bare metal infrastructure in Kyiv combines Tier-3 certified electrical redundancy with high-capacity European transit routing, empowering engineering teams to operate high-availability systems with complete predictability.
100% Dedicated Physical Silicon
Full bare-metal ownership with guaranteed CPU execution units, ECC DDR4/DDR5 memory channels, and no hypervisor steal time.
Tier-III Kyiv Data Center Resilience
Dual 10kV substation feeds, 2N online double-conversion UPS battery banks, and on-site diesel generators ensuring 99.98% power uptime.
Sub-2ms Domestic UA-IX Routing
Direct unmetered 1Gbps peering through UA-IX, GigaNet, and DTEL-IX keeping Ukrainian domestic traffic ultra-fast and sovereign.
Enterprise NVMe Gen4 Storage
Ultra-fast PCIe storage arrays delivering sustained write IOPS and rapid database commit speeds without cloud I/O throttling.
Whether supporting enterprise ERP software, high-throughput PostgreSQL/MySQL clusters, containerized Kubernetes microservices, or media streaming platforms, Ukrainian bare metal hardware delivers raw compute performance unencumbered by cloud licensing surcharges or hypervisor contention.
Dedicated Server Architecture & Telemetry Matrix
The following telemetry matrix contrasts dedicated bare-metal infrastructure in Kyiv against multi-tenant cloud virtual machines across key performance and reliability metrics:
| Architectural Layer | Multi-Tenant Cloud VPS | Onlive Server Ukraine Bare Metal |
|---|---|---|
| CPU Scheduling | Hypervisor Time-Slicing (vCPU Steal > 5%) | 100% Dedicated Physical Cores (0.0% Steal) |
| Memory Allocation | Shared memory bus, potential swap contention | Dedicated Multi-Channel ECC DDR4/DDR5 |
| Disk I/O Throughput | Throttled virtual disk (5,000 – 15,000 IOPS) | Unthrottled NVMe RAID (400,000+ IOPS) |
| Network Peering | Virtual NIC over shared transit pipeline | Direct 1Gbps Port to UA-IX & GigaNet Exchange |
| Out-of-Band Control | Browser VNC console (limited OS rescue) | Dedicated Hardware IPMI 2.0 / iDRAC with KVM |
Related Technical Deep-Dives
Expand your Ukrainian server infrastructure expertise across our connected technical cluster:
Frequently Asked Questions
What is UA-IX peering and why does it matter for servers in Ukraine?
How does GigaNet peering complement UA-IX on Kyiv dedicated servers?
What ping latency should users in Lviv, Kharkiv, and Odesa expect from a Kyiv dedicated server?
Does domestic Ukrainian peering protect against international submarine cable cuts?
Can I advertise my own Autonomous System (AS) number and BGP prefixes on an Onlive Server Kyiv node?
How does local peering improve Time-To-First-Byte (TTFB) for Ukrainian e-commerce shoppers?
Is unmetered domestic bandwidth included with Onlive Server UA-IX peering ports?
What hardware network interface cards (NICs) are deployed for UA-IX gigabit uplinks?
Deploy High-Performance Ukraine Bare Metal Dedicated Servers
Experience unthrottled bare-metal performance in Kyiv with Onlive Server starting from just $69/month. Equipped with pure NVMe storage, 1Gbps unmetered bandwidth on UA-IX, N+1 diesel generator power resilience, and dedicated IPMI console access.
Explore Ukraine Dedicated Server Plans →