
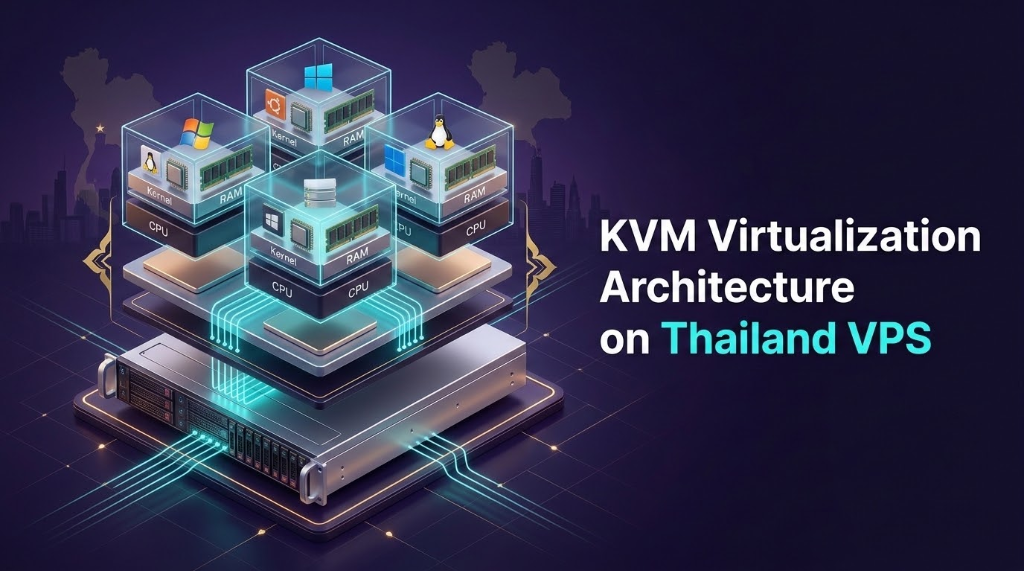
Why Is KVM Virtualization Critical for Thailand Cloud VPS Hosting?
KVM (Kernel-based Virtual Machine) virtualization is critical for a Thailand VPS because it provides complete hardware-level isolation with 100% dedicated vCPU cores and RAM. Unlike container-based virtualization like OpenVZ, KVM prevents noisy-neighbor resource throttling, supports custom Linux kernel modules, and ensures sustained high-speed domestic throughput across Bangkok datacenters.
When deploying production web applications, high-concurrency payment gateways, or transactional e-commerce platforms in Bangkok, your underlying hypervisor architecture determines system stability under peak traffic. Many server buyers select a cloud plan based on advertised vCPU and RAM without verifying hardware isolation at the hypervisor boundary. Selecting KVM-virtualized Thailand VPS hosting stationed directly inside Bangkok’s premier telecom exchanges guarantees that your virtual instance functions as an independent, bare-metal hardware partition, completely protected from adjacent tenant bursts and fully optimized for local BKNIX transit networks.
✔ Key Architectural Takeaways
- Silicon-Enforced Isolation: KVM utilizes hardware CPU virtualization extensions to execute guest instructions directly on physical processor cores, bypassing shared-kernel emulation penalties.
- Zero CPU Steal Degradation: Dedicated vCPU scheduling isolates your compute cycles, preventing noisy neighbors from hijacking clock cycles during high-traffic Thai business hours.
- Guaranteed Memory Allocation: Unlike container hosts that utilize dynamic RAM ballooning to oversell memory, KVM maps 100% of your provisioned RAM into dedicated physical ECC pages.
- VirtIO Paravirtualized I/O: Direct ring-buffer communication bypasses emulated legacy hardware, unlocking native PCIe NVMe read/write speeds exceeding 100,000 IOPS.
- Full Kernel Autonomy: Run custom Linux kernels, enable advanced TCP congestion algorithms (Google BBR), mount WireGuard VPN interfaces, or deploy nested Docker clusters without host restrictions.
Table of Contents
- Understanding KVM Virtualization in Modern Thai Datacenters
- KVM vs. Container Virtualization: The Battle for Dedicated RAM
- Hardware-Level Isolation: Preventing Noisy Neighbors in Bangkok Multi-Tenant Nodes
- VirtIO Drivers and NVMe Throughput Acceleration
- Custom Kernels, WireGuard & Docker Support Under KVM
- Benchmarking CPU Steal and Memory Allocation on Thailand Cloud VPS
- Choosing the Right KVM Plan for Thai Business Workloads
- Frequently Asked Questions (FAQ)
1
The virtualization architecture underlying your virtual server dictates its operational reliability, security boundaries, and peak resource throughput. Across Bangkok’s primary carrier facilities such as CAT Tower Bangrak, True IDC, and AIS D-Data Center, infrastructure providers historically deployed container-based virtualization like OpenVZ to cram dozens of virtual instances onto shared host nodes.
Kernel-based Virtual Machine (KVM) represents a fundamental technological departure from shared-kernel systems. Integrated directly into the mainline Linux kernel, KVM transforms a bare-metal Linux host into an enterprise Type-1 hypervisor. When paired with QEMU, KVM provisions a complete virtualized hardware environment—including a virtual BIOS, dedicated virtual CPUs (vCPUs), isolated memory address spaces, virtualized PCIe controllers, and paravirtualized network interfaces.
In a true KVM environment deployed on enterprise hardware (such as Intel Xeon Scalable or AMD EPYC processors), each guest operating system executes its own unmodified kernel. Whether deploying Ubuntu 24.04, AlmaLinux 9, Debian 12, or Windows Server 2022, your guest operating system communicates directly with physical silicon through Intel VT-x or AMD-V virtualization extensions. The hypervisor mediates physical hardware access via hardware-assisted second-level address translation (SLAT / EPT), ensuring that guest instructions execute with near-bare-metal speed.
For organizations operating within Thailand, this architectural independence is paramount. When hosting database-driven applications, payment gateways, or transactional APIs, hardware-level virtualization ensures that your compute environment remains completely autonomous. Performance is governed strictly by the dedicated physical allocations assigned to your instance, rather than fluctuating with the burst activities of adjacent cloud tenants.
2
To understand why production systems struggle on budget hosting platforms, system administrators must examine how operating memory is handled across different virtualization paradigms. Operating system-level containerization (represented historically by OpenVZ and modern shared LXC hosts) shares a single Linux kernel across every tenant on the physical machine.
Because all tenants share the host kernel, memory is managed via dynamic memory overcommitment. Budget providers in Bangkok often exploit this shared architecture through dynamic memory ballooning to oversell host capacity. When an unexpected traffic surge occurs on a Thai e-commerce store, the container demands that memory back, but if the physical host memory is exhausted, the Linux Out-Of-Memory (OOM) killer abruptly terminates active database or web server processes.
In contrast, full KVM virtualization provisions dedicated physical RAM. When ordering an 8 GB or 16 GB KVM VPS from OnliveServer in Bangkok, the hypervisor reserves that exact quantity of physical DDR4 or DDR5 ECC registered memory on the host motherboard, ensuring that 100% of your allocated RAM remains permanently pinned to your virtual instance.
| Architectural Dimension | KVM Full Virtualization | Shared Container Hosting (OpenVZ/LXC) |
|---|---|---|
| Hypervisor Type | Type-1 Bare-Metal (Kernel Module) | OS-Level Shared Kernel |
| Kernel Isolation | 100% Dedicated Guest Kernel | Shared Host Kernel (Locked) |
| RAM Allocation Model | Dedicated Physical ECC Pages | Dynamic Memory Ballooning / Overcommit |
| CPU Scheduling & Steal | Hard-Pinned vCPUs (0.0% Steal) | Time-Sliced Shared Schedulers (High %st) |
| Storage Acceleration | Native VirtIO PCIe NVMe Drivers | Shared Host Filesystem (VFS) |
| OS Compatibility | Linux, BSD, Windows Server, Custom ISO | Linux Only (Templates Dictated by Host) |
| Production Suitability | Enterprise Databases & E-Commerce | Low-Cost Staging & Dev Sandboxes Only |
For relational databases like MySQL, PostgreSQL, and Redis, dedicated memory allocation is essential. These database engines rely on massive in-memory caching mechanisms—such as MySQL’s innodb_buffer_pool_size—to keep active indexing trees and query result sets stored in RAM. If the underlying virtualization layer balloons memory out from under the database process, query response times plummet as disk reads spike.
3
A recurring complaint among technical teams deploying on low-cost cloud hosting in Thailand is the “noisy neighbor” syndrome. In shared multi-tenant environments lacking hard silicon isolation, a single tenant executing CPU-intensive tasks can saturate host CPU threads, dragging down performance for every other customer sharing that physical node.
KVM completely mitigates this vulnerability through hardware-level instruction isolation and strict Linux kernel control groups (cgroups v2). On our Bangkok enterprise virtualization clusters, physical CPU execution is governed by advanced CFS (Completely Fair Scheduler) quotas and dedicated core pinning:
Locking vCPU execution directly to dedicated physical execution units prevents adjacent tenant spikes from stealing compute cycles, while IOMMU tables shield customer memory.
This hardware isolation is crucial for organizations adhering to the Thailand Personal Data Protection Act (PDPA B.E. 2562). Under PDPA Section 37, data controllers are legally mandated to deploy adequate technical security safeguards. Hosting customer databases on hardware-isolated KVM nodes provides the verified memory segregation required to satisfy compliance audits in Bangkok.
4
Early full virtualization implementations suffered from an I/O performance bottleneck known as device emulation. In legacy virtual machines, the hypervisor emulated physical hardware, triggering CPU traps and context switches as the hypervisor simulated physical registers. To optimize physical I/O throughput alongside hardware-level virtualization, review our comprehensive NVMe storage benchmarks for Thailand VPS to achieve maximum enterprise database performance. For a comprehensive architectural breakdown of CPU instruction traps, memory overcommit behaviors, and virtio device drivers, review the official Linux Kernel KVM documentation.
Modern KVM virtualization resolves this latency overhead entirely through VirtIO paravirtualization. VirtIO is a standardized abstraction layer for high-performance virtual I/O devices. Instead of emulating physical registers, VirtIO provides cooperative device drivers inside the guest kernel that communicate directly with the host hypervisor through shared memory ring buffers:
virtio_blk/virtio_scsi: Connects guest file systems directly to enterprise PCIe NVMe storage arrays in our Bangkok datacenter, slashing I/O latency to under 0.15 milliseconds and delivering random 4K write throughput exceeding 85,000 IOPS.virtio_net: Provides multi-queue network packet processing that bypasses hypervisor software emulation, enabling line-rate 1Gbps to 10Gbps packet forwarding directly to the Bangkok Neutral Internet Exchange (BKNIX).
VirtIO acceleration unlocks the raw speed of our Bangkok datacenter’s enterprise NVMe arrays, ensuring that high-concurrency database queries execute without disk wait delays (%wa).
5
One of the most debilitating limitations of legacy container hosting is the total inability to modify the Linux kernel. In container environments, the host provider locks the kernel to prevent individual tenants from compromising host stability. As a direct consequence, users cannot install modern networking modules, mount VPN interfaces, or customize network packet schedulers.
Because an OnliveServer Thailand KVM instance provides a 100% independent virtual machine, you have complete root access to the guest operating system kernel. This architectural flexibility enables advanced engineering capabilities essential for modern production environments:
1. High-Performance WireGuard VPN Termination
WireGuard is an extremely fast, cryptographically modern VPN protocol built directly into the Linux kernel. On container hosting, WireGuard fails to initialize because containers lack permission to create tun/tap devices or load the wireguard.ko kernel module. Under KVM, WireGuard initializes natively, allowing engineering teams to build private encrypted backbones linking Bangkok corporate offices to cloud databases with wire-speed throughput.
2. Native Docker, Containerd, and Kubernetes Support
Modern microservice architectures rely heavily on container runtimes. Running Docker inside a container-based VPS (Docker-in-LXC) is notoriously unstable and frequently breaks due to nested cgroup permission errors and storage driver conflicts. KVM provides full nested virtualization support and private cgroup v2 namespaces, allowing you to run Docker CE, Docker Compose, and lightweight Kubernetes distributions (k3s, microk8s) with complete isolation.
3. Advanced TCP Stack Optimization (Google BBR)
Network latency across mobile carriers in Thailand (such as AIS, TrueMove H, and DTAC) can fluctuate due to wireless packet retransmission. Under KVM, system administrators can enable Google’s BBR (Bottleneck Bandwidth and RTT) congestion control algorithm to maximize bandwidth throughput across Thai cellular networks:
This single kernel optimization, impossible under shared container hosting, slashes time-to-first-byte (TTFB) and accelerates asset loading for Thai mobile shoppers navigating high-traffic e-commerce storefronts.
6
A rigorous engineering practice requires verifying that your cloud instance is delivering the exact compute performance you are paying for. When onboarding a new server in Thailand, administrators should execute a standardized telemetry audit to confirm hypervisor isolation, monitor CPU steal metrics, and test memory allocation under sustained load. Understanding the fundamental virtualization tier is critical when evaluating multi-tenant virtual private server architecture across Southeast Asian cloud regions.
First, verify that your virtual machine environment identifies as genuine KVM hardware virtualization rather than a shared container:
Next, monitor CPU steal time (%st) under an active compute benchmark. CPU steal indicates the percentage of time that your virtual CPU was ready to execute instructions but was forcibly stalled by the host hypervisor to service adjacent tenants:
In the rightmost column (st), an OnliveServer KVM instance maintains a rock-solid 0% CPU steal value throughout the stress test. On oversold container nodes in Bangkok, this steal metric routinely spikes to 15%–40%, severely degrading query execution and leading to sporadic application timeouts.
7
Selecting the appropriate KVM cloud plan requires matching your specific software stack, database concurrency, and visitor traffic patterns with allocated compute resources in Bangkok. Below is an architectural sizing framework tailored to business operations across Thailand and the CLMV region:
Recommended Workload Allocations
- Entry-Tier Business Apps (2 vCPU / 4 GB RAM / 60 GB NVMe): Ideal for corporate WordPress sites, agency portfolios, internal Nextcloud storage, and lightweight CRM portals serving up to 50,000 monthly Thai visitors.
- High-Concurrency E-Commerce (4 vCPU / 8 GB RAM / 120 GB NVMe): Tailored for WooCommerce, Magento, and OpenCart stores integrating Thai payment gateways (PromptPay, 2C2P, Omise). Dedicated RAM preserves InnoDB buffer pools and handles flash-sale traffic spikes smoothly.
- Algorithmic Trading & FinTech (4 vCPU / 8 GB RAM / Windows Server 2022): Designed for 24/7 MetaTrader 4/5 (MT4/MT5) terminals, automated trading bots, and FIX API connections requiring low-latency network routes to regional brokers.
- Enterprise Microservices & SaaS (8 vCPU / 16 GB – 32 GB RAM / 240+ GB NVMe): Engineered for multi-tenant SaaS backends, Docker microservice swarms, PostgreSQL clusters, and real-time WebSocket communication platforms.
By coupling genuine KVM hardware virtualization with enterprise hardware stationed directly inside Bangkok’s premier telecom interchanges, development teams and enterprise IT directors eliminate the volatility of oversold hosting, ensuring rock-solid stability, sub-15ms domestic latency, and total data sovereignty.
8
Deploy High-Performance KVM Thailand VPS in Bangkok
Eliminate CPU steal time and guarantee dedicated hardware isolation for your production applications. Benefit from pure enterprise NVMe storage, 1Gbps unmetered domestic bandwidth via BKNIX, and sub-15ms connectivity across Thailand.