

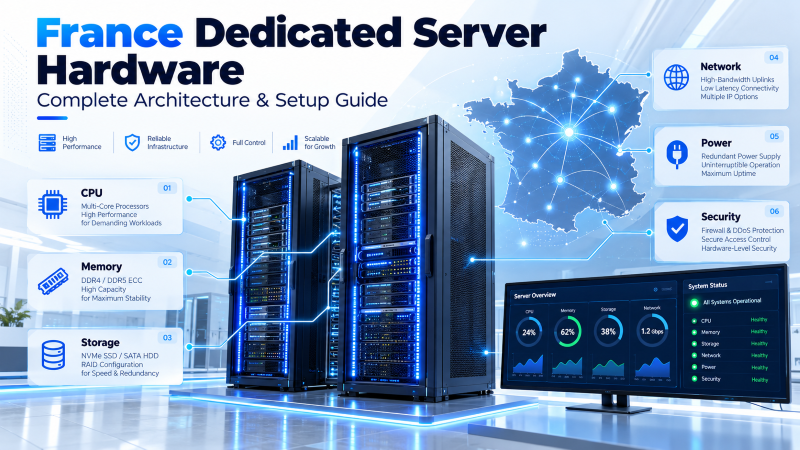
France dedicated server hardware architectures eliminate hypervisor contention by delivering 100% unshared bare-metal compute. Specifically, platforms leverage AMD EPYC 9004 or Intel Xeon 5th Gen processors, PCIe 5.0 NVMe arrays, and direct France-IX Paris exchange peering. Furthermore, deploying within Tier-3 carrier-neutral facilities in Paris and Marseille secures sub-10ms Western European transit. In addition, organizations maintain absolute compliance with EU GDPR mandates and sovereign Commission Nationale de l’Informatique et des Libertés (CNIL) data security standards.
Deploying enterprise France dedicated server hardware represents the definitive upgrade for mission-critical applications. Specifically, modern platforms outgrow multi-tenant public cloud virtual machines due to virtualization overhead. Furthermore, demanding digital services—including financial systems, transactional databases, and gaming engines—require uncompromised physical throughput. In addition, bare-metal hardware eliminates noisy-neighbor disk contention and virtualization translation layers that degrade European operations.
Specifically, infrastructure architects select French datacenters because Paris forms a vital communications gateway. For example, Paris directly connects Western Europe, Southern Europe, and Mediterranean submarine cable routing. Furthermore, organizations deploying our best France dedicated server services achieve deterministic silicon execution. In addition, unshared bare metal guarantees predictable cache hierarchies and verified physical hardware security.
France Dedicated Server Hardware: AMD EPYC & Intel Xeon Silicon Architecture
Specifically, selecting the appropriate bare-metal compute engine requires evaluating instruction pipelines, memory channel saturation, and multi-threaded scaling under high production concurrency. Therefore, dedicated server platforms in France leverage enterprise-grade silicon engineered for datacenter reliability, Level 3 cache buffers, and hardware cryptographic isolation.
Consequently, engineering teams can configure their bare-metal clusters using either high-density AMD EPYC 9004 series processors or frequency-optimized Intel Xeon Scalable 5th Gen Emerald Rapids silicon. AMD platforms provide unprecedented total core counts and 12-channel DDR5 memory controllers, which significantly accelerate parallel microservice architectures and massive virtualization nodes. Meanwhile, Intel Xeon architectures incorporate specialized hardware acceleration engines—such as Advanced Matrix Extensions (AMX) and In-Memory Analytics (IAA)—that dramatically expedite database indexing and analytical computational pipelines.
High-Density AMD EPYC vs Frequency-Optimized Intel Xeon Processors
Ultimately, matching silicon architecture to production database patterns ensures predictable system throughput without unexpected resource starvation. Furthermore, businesses operating on constrained initial budgets can also evaluate our budget-friendly VPS hosting solutions as an agile staging ground before transitioning their primary production databases onto dedicated bare-metal nodes.
Sub-Millisecond Storage Subsystems: NVMe RAID Arrays & ZFS Storage Pools
Undeniably, storage input/output bottlenecks represent the most prevalent operational barrier to achieving consistent web application responsiveness. In contrast, modern dedicated servers utilize direct-attached enterprise NVMe solid-state drives operating on PCIe 4.0 and PCIe 5.0 protocols, completely eliminating multi-tenant controller arbitration.
Consequently, deploying enterprise NVMe solid-state drives delivers sustained write latencies below 30 microseconds and over 1.2 million random 4K read IOPS. In addition, system administrators can implement either dedicated hardware RAID controllers with non-volatile flash-backed write caches (FBWC) or software-defined ZFS storage pools. While hardware RAID offloads parity computations entirely from the host CPU, ZFS introduces self-healing filesystem mechanics, inline LZ4 compression, and dynamic Adaptive Replacement Cache (ARC) stored in physical RAM.
Hardware NVMe RAID vs Software ZFS Storage Architectures
-
⚡
Dedicated Hardware Engine: Parity calculations are handled entirely on the dedicated RoC, resulting in zero host CPU overhead during heavy rebuilds.
-
🔒
8GB Flash-Backed Cache: Write-back caching features supercapacitor protection. Therefore, it guarantees zero data loss during power outages.
-
📊
Predictable Latency: Consistent write latency stays under 25 microseconds. Consequently, it is premier for ACID-compliant databases.
-
🛠️
Automated Drive Hot-Spares: Hardware auto-rebuild initiates instantly. Furthermore, it requires no manual kernel intervention.
-
🛡️
End-to-End Checksumming: Automatic checksum verification detects and repairs silent data bit rot on the fly using redundancy mirrors.
-
⚡
Adaptive Replacement Cache (ARC): ZFS dynamically utilizes system DDR5 RAM as a high-speed cache. As a result, frequent queries return at sub-microsecond latency.
-
📸
Atomic Snapshot Trees: Create instantaneous copy-on-write snapshots. In addition, live production database writes remain unlocked.
-
🗜️
Inline LZ4 Compression: Transparent filesystem compression reduces drive write amplification. Moreover, it expands effective capacity by 35%.
As a result, selecting between hardware RAID and software ZFS pools depends primarily on whether your application architecture prioritizes strict hardware-offloaded write determinism or software-defined snapshot flexibility. For instance, high-concurrency payment processing platforms benefit substantially from hardware-backed write caching, whereas content repositories and containerized microservice registries leverage ZFS inline compression and atomic snapshots to optimize storage density.
Paris Datacenter Infrastructure: France Dedicated Server Hardware Peering
Furthermore, datacenter geography and network transit engineering determine the ultimate responsiveness of any digital platform operating across the European single market. France occupies a uniquely advantageous topological position within the European telecommunications grid, functioning as the primary terrestrial bridge between northern European internet exchanges and Mediterranean subsea gateways. Furthermore, hosting physical hardware in Paris ensures proximity to central internet exchanges while avoiding congested transatlantic network segments.
Consequently, our bare-metal infrastructure is stationed within certified Tier-3 facilities—including Telehouse Voltaire (TH2) and Equinix Saint-Denis (PA2/PA3)—in the greater Paris metropolitan area. These campuses feature direct cross-connects to the France-IX Paris exchange, where over one thousand international transit providers and networks peer directly. Indeed, direct peering completely bypasses intermediate transit networks, securing average round-trip times below 8 milliseconds to major European economic hubs.
Moreover, carrier-neutral multi-homing prevents upstream fiber disruptions from impacting users. For example, automated BGP routing protocols immediately redirect packet flow across alternate Tier-1 transit backbones in sub-second intervals. Therefore, your European end users never experience connection timeouts. Consequently, media streaming quality and e-commerce checkout sessions remain uninterrupted.
Linux Kernel Tuning & LACP Bonding: France Dedicated Server Hardware
Unlocking the complete throughput potential of bare-metal hardware requires precise operating system kernel optimization. However, enterprise dedicated servers handle tens of thousands of concurrent TCP sockets. Therefore, administrators must optimize kernel socket buffers, expand backlog queues, and implement network interface card bonding.
Specifically, configuring dual 10GbE or 25GbE network interface cards using IEEE 802.3ad LACP doubles aggregate throughput. In addition, this network bonding guarantees zero-downtime physical link failover. Furthermore, applying custom sysctl parameters optimizes TCP window scaling. As a result, TCP BBR congestion control prevents memory swapping during sudden database memory surges.
Consequently, executing these kernel configurations ensures that your physical network stack can process millions of concurrent packets per second without encountering packet buffer drops or CPU interrupt saturation. Furthermore, combining TCP BBR congestion control with carrier-neutral Paris routing guarantees maximum throughput across long-distance European and transatlantic client connections.
Hardware Specification Matrix & Enterprise Workload Qualification
In addition, selecting the optimal bare-metal configuration requires evaluating specific application resource requirements against physical hardware boundaries. Specifically, analytical workloads require high memory density and PCIe lanes, whereas e-commerce platforms depend heavily on sustained clock frequencies and redundant NVMe storage arrays.
In order to streamline your infrastructure procurement process, the following qualification matrix outlines four standard production configurations deployed across our Paris datacenters. Each configuration is specifically calibrated for target production workloads, verified for thermal stability, and connected via redundant uplink network topologies.
As a result, engineering leads can select an exact hardware tier that satisfies their concurrency requirements. Furthermore, this qualification matrix preserves an effortless upgrade pathway to higher core-density architectures as application traffic scales across Europe.
Step-by-Step Hardware Provisioning & Security Hardening Pipeline
Specifically, securing bare-metal infrastructure requires a structured deployment methodology executed before publishing production endpoints to public DNS records. Because physical servers possess low-level hardware controllers, proper operational security begins at the BMC firmware layer and extends through the operating system partition layout.
Therefore, following a standardized five-stage provisioning pipeline guarantees that your French dedicated server adheres to international defense-in-depth security best practices. The following operational checklist details the essential deployment sequence verified by our datacenter engineering team.
Production Server Hardening & Deployment Sequence
Consequently, completing this structured implementation pipeline ensures your bare-metal server maintains robust defenses against network intrusion, automated vulnerability scanners, and unexpected hardware subsystem failures.
Regulatory Compliance, CNIL Standards & Sovereign Data Governance
Moreover, operating infrastructure within the European Union requires compliance with data privacy laws and sovereignty directives. In particular, the EU General Data Protection Regulation (Regulation 2016/679) mandates strict physical security. Furthermore, organizations processing European citizen data must guarantee verifiable access controls and transparent geographic storage boundaries.
Consequently, the French regulatory authority—the Commission Nationale de l’Informatique et des Libertés (CNIL)—enforces strict guidelines. For example, CNIL regulates data sovereignty, cryptographic retention, and foreign extraterritorial subpoena exposure. Therefore, deploying dedicated servers in Paris or Marseille ensures databases remain under French jurisdiction. As a result, organizations eliminate legal risks associated with non-European cloud hypersonics.
Therefore, international enterprises and French domestic organizations achieve total regulatory peace of mind when hosting their mission-critical applications on dedicated bare-metal hardware in France.
Frequently Asked Questions
Q
What makes France dedicated server hardware superior to virtual cloud instances?
What makes France dedicated server hardware superior to virtual cloud instances?
Unlike virtual cloud instances that share physical resources, France dedicated servers provide 100% unshared bare-metal hardware. Consequently, this eliminates hypervisor virtualization overhead entirely. Furthermore, it guarantees sub-millisecond I/O latency and grants full low-level root access for custom kernel tuning.
Q
How does direct France-IX peering reduce application latency?
How does direct France-IX peering reduce application latency?
Specifically, France-IX is the leading Internet Exchange Point in France. In addition, it interconnects over one thousand telecommunications providers and content networks. Therefore, our Paris dedicated servers peer directly at France-IX. As a result, network packets reach Western European users at sub-8ms latency without traversing congested hops.
Q
Can I choose between AMD EPYC and Intel Xeon processors?
Can I choose between AMD EPYC and Intel Xeon processors?
Yes. Specifically, we offer both AMD EPYC 9004 processors and Intel Xeon Scalable 5th Gen platforms. For instance, AMD EPYC chips deliver up to 96 cores and 12-channel DDR5 memory for multi-threaded concurrency. In contrast, Intel Xeon Emerald Rapids processors excel in frequency-sensitive transactional databases and Intel AMX workloads.
Q
What out-of-band remote management tools are included?
What out-of-band remote management tools are included?
In addition, every dedicated server includes IPMI 2.0 or iDRAC9 hardware on an isolated private network. Consequently, system administrators can configure BIOS settings and mount virtual ISO media remotely. Furthermore, engineers can monitor thermal sensors and execute hard power recycles even if the primary operating system crashes.
Q
Are hardware RAID controllers available with NVMe drive arrays?
Are hardware RAID controllers available with NVMe drive arrays?
Yes. Specifically, you can configure Broadcom MegaRAID 9560-8i controllers with 8GB flash-backed write cache for hardware NVMe arrays. Alternatively, you can deploy software-defined ZFS storage pools over direct PCIe lanes. As a result, ZFS delivers self-healing filesystem integrity without requiring dedicated RAID silicon.
Q
How does hosting in France assist with EU GDPR and CNIL compliance?
How does hosting in France assist with EU GDPR and CNIL compliance?
Consequently, hosting in Paris or Marseille ensures all data physically resides within French national territory. Therefore, deployments comply fully with EU GDPR Regulation 2016/679 and CNIL directives. In addition, this sovereign hosting insulates corporate data from non-EU extraterritorial search warrants.
Q
What DDoS protection capabilities are included with the dedicated hardware?
What DDoS protection capabilities are included with the dedicated hardware?
Furthermore, all network uplinks are shielded by automated multi-layer hardware DDoS mitigation systems. Specifically, our scrubbing centers inspect incoming network traffic in real time at the edge. Consequently, the mitigation infrastructure neutralizes volumetric floods and Layer-7 attacks up to multi-terabit capacity within milliseconds.
⚡ Sub-8ms Western Europe Latency
🔒 ISO 27001 & Tier-3 Certified Datacenter
