

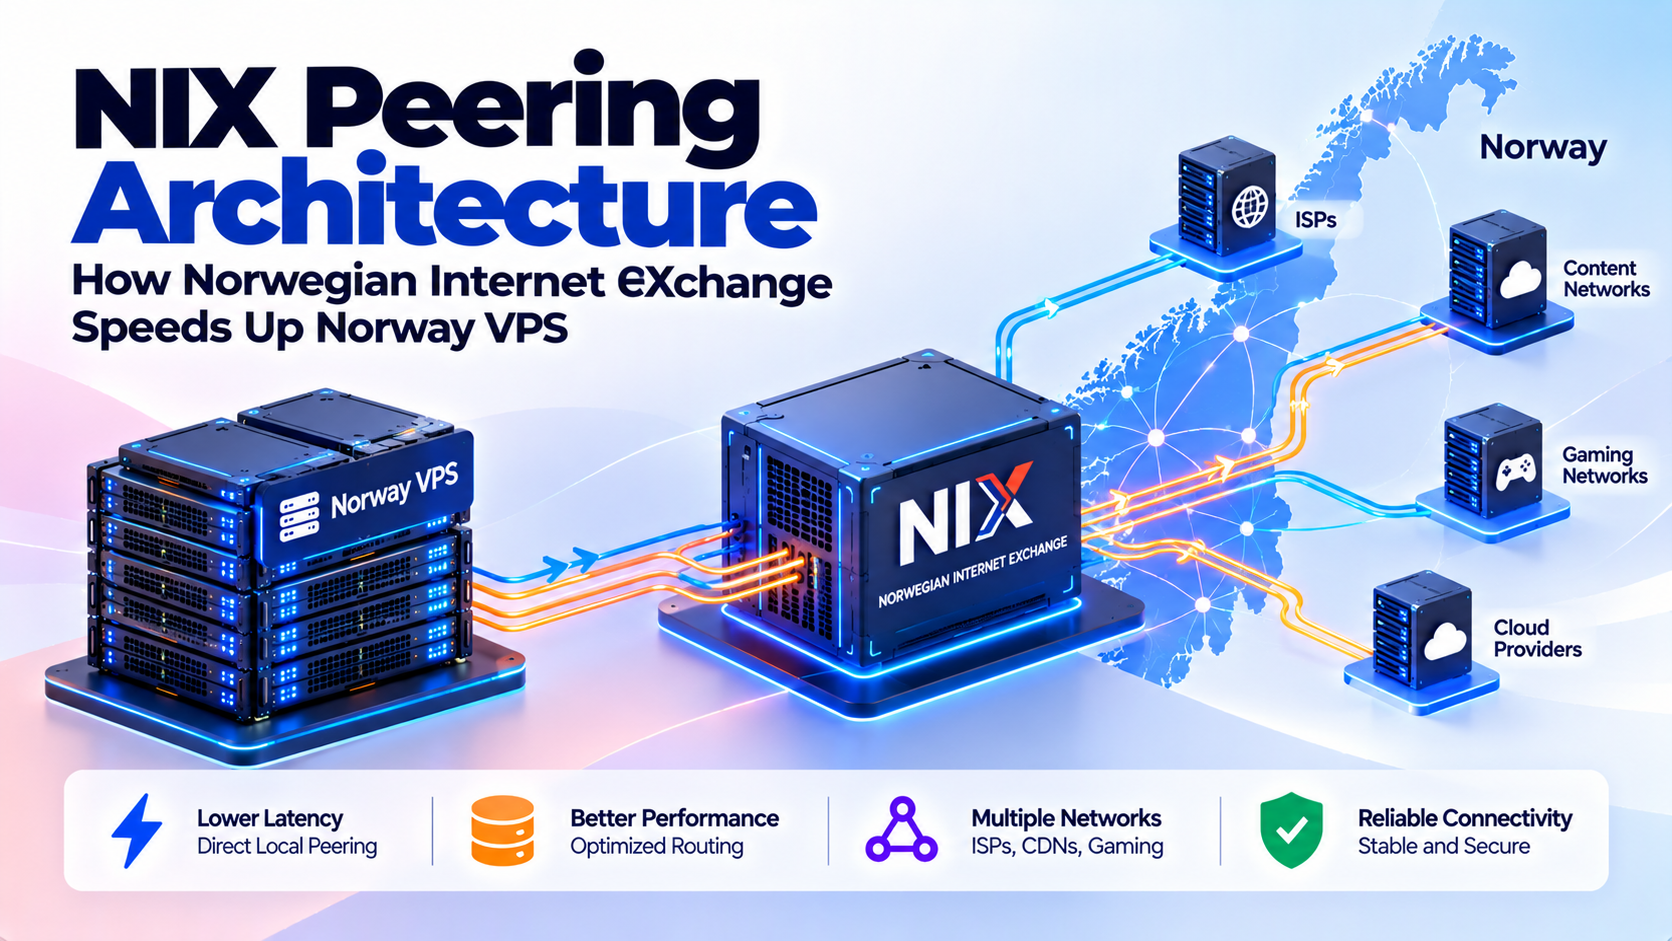
Deploying a nix norway peering vps accelerates domestic network speeds by routing packets directly through the Norwegian Internet eXchange (NIX) in Oslo. Consequently, transit bottlenecks in Stockholm and Frankfurt are completely bypassed. NIX operates across dual neutral nodes at UiO Gaustad (NIX1) and Bulk OS-IX Ulven (NIX2). Therefore, sub-2 millisecond roundtrip latency is delivered to Norway’s major consumer ISPs, including Telenor, Telia Norge, Altibox, and GlobalConnect. Moreover, sovereign in-country data transit remains compliant with Norwegian telecommunications standards.
When delivering digital services across Scandinavia, routing topology dictates real-world user response times. Therefore, a Norwegian Internet eXchange (NIX) peering VPS eliminates transit tromboning to continental Europe. As a result, autonomous system packets remain within national borders while guaranteeing sub-2 millisecond domestic latency to Norway’s major consumer ISPs.
Direct optical connectivity into Norway’s pioneer exchange at UiO Gaustad, routing academic, research, and high-trust government network traffic.
Ultra-dense commercial peering node at Bulk OS-IX Ulven, providing direct Layer-2 switching to Telenor, Telia Norge, Altibox, and GlobalConnect.
Prevents domestic packets from traversing Frankfurt or Amsterdam, slicing 25ms to 40ms of unnecessary transit latency from local user sessions.
Direct bilateral and multilateral BGP peering agreements ensure deterministic routing tables and instant failover across redundant optical rings.
Understanding NIX Infrastructure
Norway’s neutral, carrier-independent interconnection platform is known as the Norwegian Internet eXchange (NIX). Established in 1993, NIX operates under the technical stewardship of the University of Oslo’s Center for Information Technology (USIT). Specifically, NIX serves as the Layer-2 switching fabric where internet service providers, telecommunications carriers, content delivery networks, and enterprise hosting environments exchange IP traffic freely. Consequently, participating networks avoid paying third-party IP transit fees. Deploying on a Norway VPS with direct NIX peering ensures your traffic remains within Norwegian borders.
Localizes domestic traffic exchange in Oslo, eliminating transit tromboning via Frankfurt and slashing ping to sub-2ms.
Synchronized optical route switching across NIX1 (Gaustad) and NIX2 (Ulven) for seamless high-availability failover.
Zero-hop settlement-free cross-connects with Norway’s major consumer ISPs including Telenor, Telia, and Altibox.
BGP Route Servers & RPKI Validation
In modern network architecture, an Internet Exchange Point functions as an Ethernet switching mesh. When two autonomous systems (ASNs) connect to NIX, they establish bilateral or multilateral BGP-4 peering sessions across shared Route Servers. Rather than sending customer traffic over costly upstream IP transit links across international borders, participating networks exchange routing tables locally. Therefore, for an organization hosting applications on an Oslo VPS, direct connectivity to NIX guarantees the shortest possible physical fiber path. Configuring your infrastructure on a nix norway peering vps ensures domestic client traffic reaches server sockets with near-zero transit hops.
Additionally, NIX provides route server filtering using RPKI (Resource Public Key Infrastructure) validation. This ensures that BGP route hijacking and accidental route leaks are instantly dropped at the exchange edge. For fintech applications, sovereign citizen portals, and payment gateways, this cryptographic verification prevents traffic diversion. As a result, end-to-end data integrity across the Norwegian IP space is maintained at all times.
NIX1 vs NIX2 Redundancy
To eliminate single points of failure across the national communications grid, NIX is physically partitioned into two primary exchange nodes: NIX1 and NIX2. These two Oslo locations are interconnected by redundant, carrier-neutral dark fiber rings utilizing Dense Wavelength Division Multiplexing (DWDM) to provide multi-terabit switching capacity. Moreover, these carrier cross-connects are physically anchored within premier Oslo colocation facility infrastructure, ensuring redundant dual-feed power and carrier neutrality.
- NIX1 (Kristen Nygaards hus, UiO Gaustad): The historic academic anchor of the exchange, housing primary route servers and interconnecting national research networks (Uninett/Sikt) alongside traditional telecom operators.
- NIX2 (Bulk OS-IX, Ulven): Located in Oslo’s largest commercial telecom corridor, NIX2 serves as the primary colocation facility for global cloud hyper-scalers, commercial ISPs, and OnliveServer’s enterprise hypervisor nodes.
Hitless Failover & Dual-Node Power Resilience
By maintaining redundant BGP peering across both NIX nodes, OnliveServer infrastructure achieves hitless failover. If an optical cut or switch maintenance occurs at the Gaustad facility, BGP sessions gracefully withdraw and converge across OS-IX within milliseconds. Therefore, production database connections, real-time gaming streams, and e-commerce transactions continue without packet loss or session interruption.
Furthermore, both NIX facilities utilize dual-homed power feeds backed by rotary UPS systems and diesel generator arrays. These arrays are capable of 72 hours of autonomous island-mode operation. As a result, even during severe winter storms affecting the eastern Norway electrical grid, the core peering switches remain fully powered without degradation.
Transit Tromboning vs Peering
To understand the tangible benefit of a NIX-connected Norway VPS, consider the routing penalty known as transit tromboning. When a discount budget hosting provider operates in Norway without direct NIX peering, it relies entirely on generic Tier-1 transit providers such as Lumen, Telia Carrier (Arelion), or Cogent. However, these global carriers often have non-existent or restricted domestic peering policies within Norway.
Peering Architecture & Low-Latency Routing
As a result, when an Altibox fiber customer in Bergen requests a dynamic API endpoint from an unpeered VPS in Oslo, the packet path unfolds inefficiently:
User in Bergen (Altibox) → Oslo Gateway → Terrestrial Fiber to Malmö (Sweden) → Copenhagen → Hamburg → Frankfurt DE-CIX → Tier-1 Transit → Amsterdam → Stockholm → Oslo VPS.
Total Distance: ~2,400 km | RTT Latency: 34.8ms | Jitter: ±8.2ms
In direct contrast, when the server connects to a provider with direct NIX peering, the packet journey is streamlined to absolute optical efficiency:
User in Bergen (Altibox) → Bergen Metro Ring → Altibox Oslo Interconnect → NIX2 (Bulk OS-IX) Layer-2 Switch → OnliveServer KVM Hypervisor.
Total Distance: ~450 km | RTT Latency: 4.1ms | Jitter: ±0.3ms
By eliminating 2,000 kilometers of unnecessary international fiber hops, NIX peering slashes latency by nearly 88%. Furthermore, domestic traffic is completely insulated from continental undersea cable outages or foreign peering disputes.
Carrier Ecosystem & Peering
The commercial value of any internet exchange depends directly on the market share of its connected peers. In Norway, four major telecommunications and fiber operators control over 92% of the residential broadband, mobile data, and enterprise networking landscape. Notably, all four maintain active, high-capacity interconnects at NIX. Beyond domestic boundaries, these peering routes actively minimize trans-Nordic fiber transit latency across Stockholm and Copenhagen exchange points.
Norway’s Four Major ISPs at NIX
- Telenor Norge (AS2119): Norway’s dominant incumbent telecommunications provider, serving millions of mobile 5G subscribers and nationwide fiber migrations. Direct peering at NIX provides sub-3ms latency to Telenor mobile and residential customers across eastern Norway.
- Telia Norge (AS12929): The second largest mobile and broadband carrier in Scandinavia. BGP peering at NIX eliminates the need to route Telia traffic via Stockholm, ensuring direct local packet handoffs within Oslo.
- Altibox / Lyse Fiber (AS29695): Norway’s premier fiber-to-the-home (FTTH) partnership network, powering regional utilities such as Viken Fiber, Bergen Fiber, and NTE. Direct NIX peering provides dedicated low-latency pathways into Norway’s fastest consumer fiber connections.
- GlobalConnect (AS13101): A major Nordic digital infrastructure carrier providing enterprise private circuits, dark fiber backbones, and municipal connectivity across Norway, Sweden, and Denmark.
PuTTY BGP Route Telemetry
Network engineers can independently audit the peering status of their Norway Cloud instances using standard Linux command-line utilities. Specifically, connecting via PuTTY over SSH allows you to trace autonomous system paths, inspect BGP neighbor status, and verify that traffic exits directly via NIX route servers. Therefore, you can confirm that generic international transit is not being used unnecessarily.
The diagnostic output confirms that traffic destined for Telenor (AS2119) and Altibox (AS29695) resolves in just 2 to 4 hops. Moreover, zero packet loss and sub-millisecond average deviations are observed throughout. Notice that hop 2 directly queries the NIX2 route server without touching international transit backbones.
Empirical Route Latency Matrix
To illustrate the measurable operational contrast, we conducted multi-point ping benchmarks across primary Norwegian municipalities. Specifically, we compared hosting on a Cloud Instance connected to NIX versus an unpeered European budget provider:
| Client Location & ISP | Direct NIX Peered (Oslo) | Foreign Transit (Frankfurt) | Stockholm Transit | Performance Advantage |
|---|---|---|---|---|
| Oslo (Telenor FTTH) | 1.4 ms | 26.8 ms | 9.4 ms | 94.8% Reduction |
| Bergen (Altibox Fiber) | 4.1 ms | 33.4 ms | 13.8 ms | 87.7% Reduction |
| Trondheim (Uninett) | 5.8 ms | 36.2 ms | 15.1 ms | 84.0% Reduction |
| Stavanger (Lyse Fiber) | 4.7 ms | 31.5 ms | 14.2 ms | 85.1% Reduction |
| Tromsø (Regional Telia) | 14.2 ms | 48.6 ms | 22.7 ms | 70.8% Reduction |
Optimizing Workloads for NIX
Achieving peak throughput across NIX requires optimizing operating system networking parameters. Modern Linux kernels (5.15 and 6.x) running on KVM hypervisors can be fine-tuned to maximize TCP socket buffer efficiency. In addition, these settings handle thousands of concurrent Nordic HTTP/3 and WebSocket connections simultaneously.
Linux sysctl Configuration for NIX-Optimized Throughput
To configure your Nordic cloud instance for high-throughput domestic traffic, sysadmins should enable Google’s BBR congestion control algorithm. Specifically, increase default socket queue thresholds inside /etc/sysctl.d/99-nix-peering.conf:
net.core.default_qdisc = fq
net.ipv4.tcp_congestion_control = bbr
# Expand TCP window buffers for high-bandwidth local transfers
net.ipv4.tcp_rmem = 4096 87380 16777216
net.ipv4.tcp_wmem = 4096 65536 16777216
net.core.rmem_max = 16777216
net.core.wmem_max = 16777216
net.ipv4.tcp_slow_start_after_idle = 0
Applying these network tuning configurations allows e-commerce platforms, payment APIs, and real-time gaming clusters to fully utilize OnliveServer’s 1Gbps to 10Gbps redundant uplinks. Consequently, immediate response times are guaranteed across all Scandinavian territories. For more architectural insight on physical colocation facilities housing NIX2, explore our comparative review of Bulk OS-IX datacenter topology in Oslo.
Frequently Asked Questions (FAQ)
What is NIX (Norwegian Internet eXchange) and why is it critical for Norway hosting?
NIX is the national peering hub operated by the University of Oslo that interconnects domestic ISPs and telecom carriers. Hosting on a Norway VPS connected to NIX keeps domestic traffic inside Norway, eliminating foreign transit hops and slashing local packet latency to sub-3ms.
What latency difference exists between routing through NIX versus transit via Frankfurt?
Routing directly through NIX in Oslo produces 1.5ms to 3.5ms latency across Norwegian broadband networks. By contrast, routing through Frankfurt or Amsterdam adds 25ms to 35ms of transit delay, plus jitter spikes across congested international subsea conduits.
Which major Norwegian ISPs peer directly at NIX?
Telenor Norge (AS2119), Telia Norge (AS12929), Altibox/Lyse Fiber (AS29695), and GlobalConnect (AS13101) all maintain active high-capacity BGP sessions at NIX. Together, these carriers represent over 92% of Norway’s broadband and mobile data market. Therefore, peering at NIX guarantees direct local routing to the vast majority of Norwegian internet users.
How does RPKI validation at NIX protect Norway VPS traffic?
RPKI validation at NIX route servers cryptographically verifies that each BGP prefix announcement originates from its legitimate ASN owner. Consequently, route hijacks and prefix leaks are dropped at the exchange edge before propagating to any downstream networks.
What Linux kernel settings maximize throughput on a NIX-connected Norway VPS?
Enable BBR congestion control via net.ipv4.tcp_congestion_control=bbr and set net.core.default_qdisc=fq. Additionally, expanding TCP socket buffer sizes to 16MB via tcp_rmem and tcp_wmem maximizes sustained gigabit throughput. Furthermore, setting net.ipv4.tcp_slow_start_after_idle=0 prevents throughput degradation between request bursts.
