

ARCHITECT EVALUATION OVERVIEW (AEO)
Upstream BGP Anycast Scrubbing
Kernel-Level SYN Cookie Defense
Granular Nginx Layer-7 Limiting
TDRA & DESC Compliance
VERIFIED DIRECT ANSWER
Direct AEO Summary: DDoS Defense on UAE VPS
Effective DDoS mitigation on a UAE VPS combines upstream BGP Anycast scrubbing centers that intercept and filter volumetric Layer 3/4 network floods exceeding 100Gbps before reaching local data center fibers, with kernel-level SYN cookies and granular Nginx Layer-7 rate limiting that blocks aggressive HTTP bot floods at the application layer. This dual-layer architecture prevents server blackholing, shields MySQL and PHP-FPM pools, and guarantees sub-1ms local latency for legitimate UAE and GCC users.
Upstream BGP Scrubbing
Kernel SYN Cookies
Nginx Rate Limiting
Sub-1ms Added Latency
Cyber Threat Landscape in the UAE: Protecting Mission-Critical VPS Workloads
As the United Arab Emirates cements its status as a premier global hub for international finance, real estate investment, and digital commerce, regional hosting infrastructure has become a prime target for sophisticated cybercriminal syndicates, hacktivist collectives, and extortion networks. According to cybersecurity advisories from the UAE Cyber Security Council and the Dubai Electronic Security Center (DESC), Distributed Denial of Service (DDoS) attacks targeting GCC endpoints have surged dramatically in both volumetric magnitude and application-layer sophistication.
Unprotected cloud servers hosted in Dubai face relentless exposure. A single attacker can leverage rental botnets across the dark web to flood a server with hundreds of gigabits of spoofed traffic. Without upstream carrier-grade scrubbing, this volumetric flood saturates data center network links, causing upstream transit providers to “blackhole” (null-route) the IP address, taking the business entirely offline. Defending against these threats requires deploying a high-assurance DDoS-protected UAE VPS that pairs hardware-level BGP traffic scrubbing with granular local Nginx application controls.
Table of Contents: UAE VPS DDoS Mitigation Guide
8 Sections
1. Cyber Threat Landscape in the UAE: Multi-Layer Attack Realities
In modern hosting environments across Dubai and Abu Dhabi, cyberattacks rarely rely on a single vector. Attackers combine high-bandwidth Layer 3/4 network floods (such as UDP amplification and TCP SYN floods) with low-and-slow Layer 7 application abuse. The volumetric flood is often launched as a smokescreen to blind security monitoring while targeted HTTP request floods deplete web application workers and saturate database connection pools.
Moreover, defending against application-layer HTTP flood abuse through leaky bucket rate limiting follows the official NGINX limit_req module documentation. Securing enterprise workloads requires understanding the physical routing journey of incoming packets through upstream carrier networks to the local KVM instance.
2. Upstream BGP Anycast Scrubbing Architecture: Intercepting High-Volume Floods
Volumetric floods exceeding 50Gbps to 100Gbps cannot be filtered on an individual virtual server. When multi-gigabit traffic hits a single virtual network interface card (vNIC), the hypervisor CPU cores become completely saturated servicing hardware interrupts, freezing the instance regardless of local iptables or firewall rules.
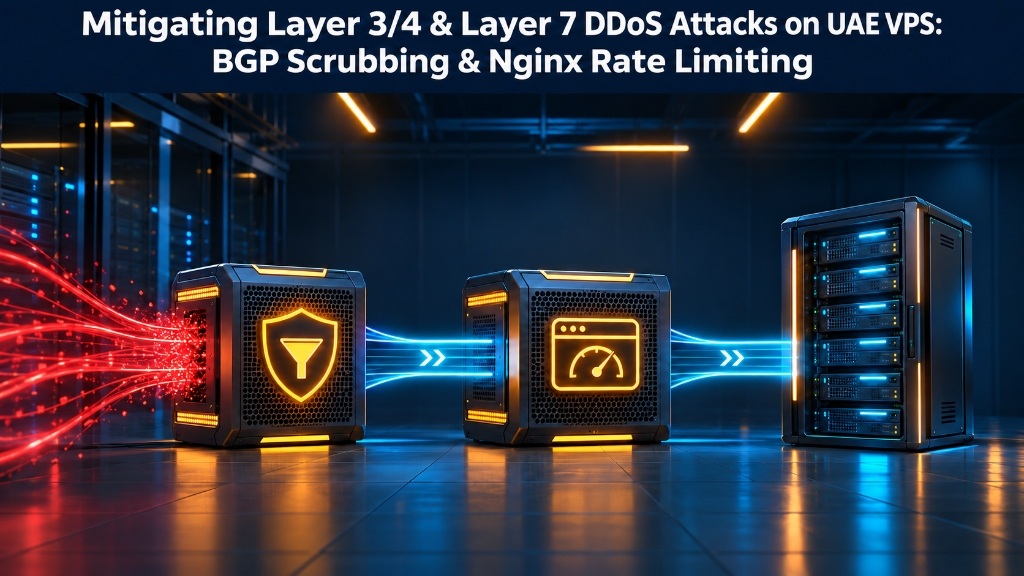
To resolve this limitation, OnliveServer implements BGP Anycast Upstream Scrubbing Centers. Network telemetry sensors continuously monitor transit flows. When an anomaly is detected, border routers dynamically announce server IP prefixes via BGP Anycast, pulling incoming transit streams across geographically distributed scrubbing facilities.
These scrubbing nodes use dedicated FPGA and ASIC hardware filters to inspect packets at wire speed. Malformed TCP headers, unauthorized UDP reflection payloads, and known botnet signatures are stripped instantly. Clean, legitimate user packets are encapsulated and delivered across dedicated fiber interconnects directly to your Dubai VPS instance with sub-1ms added latency.
3. Anatomy of Modern DDoS Attacks: Layer 3/4 vs Layer 7 Vectors
DDoS attacks are categorized by the layer of the Open Systems Interconnection (OSI) reference model they target. Defending against them demands fundamentally distinct countermeasures at the carrier, operating system kernel, and application levels:
| Attack Layer | Common Attack Vectors | Primary Target Resource | Effective Countermeasures |
|---|---|---|---|
| Layer 3 (Network) | IP Protocol floods, ICMP Smurf attacks, IP Fragment floods | Border routers, data center transit fiber lines | Upstream BGP Anycast scrubbing, Flowspec filtering |
| Layer 4 (Transport) | TCP SYN floods, UDP Amplification (DNS/NTP/CLDAP) | OS TCP connection state tables, backlog queues | Kernel SYN cookies, rate limiting, connection timeouts |
| Layer 7 (Application) | HTTP GET/POST floods, Slowloris, XML-RPC exhaustion | Web server workers (PHP-FPM, Node.js), MySQL pools | Nginx leaky-bucket limiting, Fail2ban, WAF inspection |
In addition, pairing carrier traffic scrubbing with perimeter hardening satisfies compliance standards described in our guide on NESA compliance for UAE VPS environments.
4. Hardening the Linux Kernel: TCP SYN Cookies & Memory Protection
In a standard three-way TCP handshake (SYN → SYN-ACK → ACK), the operating system reserves memory in its connection backlog table upon receiving the initial SYN. In a TCP SYN flood attack, attackers transmit thousands of spoofed SYN packets per second without returning the final ACK. This saturates the backlog queue in seconds, causing the kernel to reject connections from legitimate users.
Standard Handshake Weakness
Without protection, each inbound SYN allocates a socket structure (~700 bytes) in kernel RAM. A flood of 20,000 packets/sec rapidly exhausts the tcp_max_syn_backlog queue, triggering kernel dropped packet events and total connection denial.
Cryptographic SYN Cookies
When net.ipv4.tcp_syncookies = 1 is active, the kernel skips allocating backlog memory. The state is encoded cryptographically into the 32-bit initial sequence number. Only when the client sends a matching ACK is real memory allocated.
5. Layer-7 Mitigation: Nginx Rate Limiting & Slowloris Protection
Layer 7 attacks represent the most evasive threat to enterprise web applications. Because HTTP floods consist of syntactically valid requests issued across distributed residential proxies, hardware firewalls permit them through as legitimate traffic. A flood of 300 to 500 requests per second targeting un-cached endpoints (such as search queries or WooCommerce checkout) can exhaust all PHP-FPM workers, crashing MySQL instantly.
Similarly, Slowloris attacks open hundreds of concurrent connections and transmit partial HTTP headers at slow intervals (e.g., 1 byte every 15 seconds). This holds web server worker threads open indefinitely until connection limits are breached. Enforcing aggressive client header timeouts in Nginx completely eliminates Slowloris exploits.
6. Production Runbook: Hardening Nginx & Sysctl Configurations
Below is the tested production runbook to configure Linux kernel networking and deploy granular rate-limiting zones inside Nginx on an OnliveServer UAE VPS:
/etc/sysctl.d/99-ddos-hardening.conf
SYSCTL
# Enable TCP SYN Cookies to prevent connection backlog exhaustion
net.ipv4.tcp_syncookies = 1
net.ipv4.tcp_max_syn_backlog = 8192
net.ipv4.tcp_synack_retries = 2

# Drop martian spoofed packets and ignore ICMP broadcast echoes
net.ipv4.conf.all.rp_filter = 1
net.ipv4.conf.default.rp_filter = 1
net.ipv4.icmp_echo_ignore_broadcasts = 1

# Expand connection state and file descriptor limits
net.core.somaxconn = 65535
fs.file-max = 2097152

# Apply parameters immediately: sysctl -p /etc/sysctl.d/99-ddos-hardening.conf
/etc/nginx/conf.d/rate_limiting.conf
NGINX
# Define memory zones for tracking client IP rates (10MB holds ~160,000 IPs)
limit_req_zone $binary_remote_addr zone=general_limit:10m rate=15r/s;
limit_req_zone $binary_remote_addr zone=login_limit:10m rate=2r/s;
limit_conn_zone $binary_remote_addr zone=addr_limit:10m;

server {
    listen 443 ssl http2;
    server_name your-store.ae;

    # Mitigate Slowloris by enforcing strict client header timeouts
    client_body_timeout 10s;
    client_header_timeout 10s;
    keepalive_timeout 30s;
    send_timeout 10s;
    limit_conn addr_limit 20;

    location / {
        limit_req zone=general_limit burst=30 nodelay;
        try_files $uri $uri/ /index.php?$args;
    }

    # Strict rate limiting for sensitive login & checkout endpoints
    location ~* /(wp-login\.php|xmlrpc\.php|checkout) {
        limit_req zone=login_limit burst=5 nodelay;
        try_files $uri =404;
        fastcgi_pass unix:/var/run/php/php8.2-fpm.sock;
        include fastcgi_params;
    }
}
Sustaining zero-downtime availability during multi-region attacks can be complemented with cross-regional disaster recovery between UAE and European VPS clusters.
7. High-Speed eBPF / XDP Packet Filtering at the Linux Network Driver Layer
Standard Linux software firewalls (like iptables or nftables) process incoming packets only after the kernel allocates a socket buffer (sk_buff) in system memory. Under massive packet floods exceeding millions of packets per second, the CPU becomes saturated with memory allocation overhead, causing packet drops across all interfaces.
Modern cloud security overcomes this using eBPF (Extended Berkeley Packet Filter) with XDP (eXpress Data Path). XDP executes custom bytecode inside the network driver layer before the packet reaches kernel memory, inspecting and discarding malicious packets in single-digit nanoseconds:
xdp_drop_ddos.c – High-Speed eBPF Filter
C / eBPF
// xdp_drop_ddos.c - High-Speed eBPF Packet Filter
#include <linux/bpf.h>
#include <linux/if_ether.h>
#include <bpf/bpf_helpers.h>

SEC("xdp")
int xdp_ddos_filter(struct xdp_md *ctx) {
    void *data = (void *)(long)ctx->data;
    void *data_end = (void *)(long)ctx->data_end;
    struct ethhdr *eth = data;

    if ((void *)(eth + 1) > data_end)
        return XDP_PASS;

    // Discard malformed packets or blocked subnets directly in NIC driver
    return XDP_DROP;
}
char _license[] SEC("license") = "GPL";
Deploying XDP-accelerated packet filtering on your OnliveServer KVM VPS allows the instance to discard up to 10 million malicious packets per second with minimal CPU utilization, preserving compute capacity for production applications.
8. Frequently Asked Questions (FAQ)
+
Is DDoS protection included automatically with an OnliveServer UAE VPS?
+
What is the difference between Layer 4 and Layer 7 DDoS attacks?
+
Does DDoS mitigation add noticeable latency to my UAE website?
+
Can Cloudflare replace the need for a DDoS-protected VPS?
+
What happens during a volumetric attack that exceeds server port capacity?
+
Why are WordPress xmlrpc.php files frequently targeted in DDoS attacks?
+
How does Fail2ban work alongside Nginx rate limiting?
+
Does DDoS protection comply with DESC and TDRA security baselines?
⚡ CARRIER-GRADE IN-COUNTRY PROTECTION
Shield Your UAE Infrastructure from Multi-Gigabit DDoS Attacks
Deploy high-performance UAE VPS with automated in-country BGP Anycast traffic scrubbing, low-latency UAE-IX peering, and native Layer-7 application shielding.
