

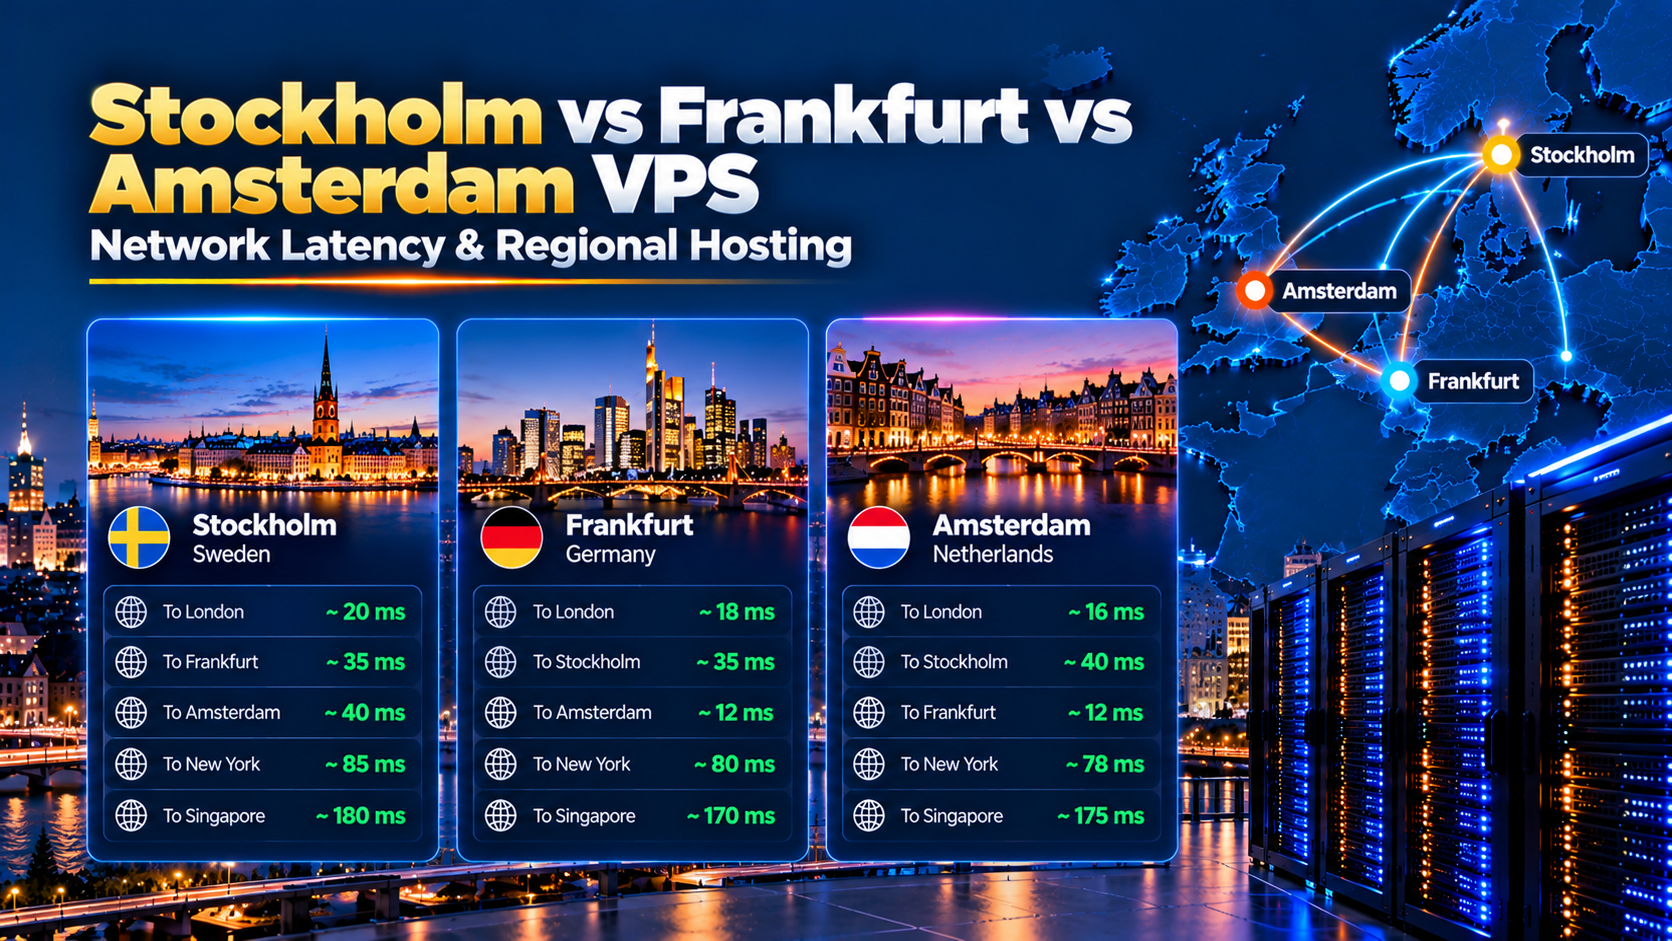
When planning an enterprise deployment for sweden vs germany vps latency, while Frankfurt and Amsterdam represent continental European transit hubs, choosing a Stockholm VPS over German hosting reduces latency to Nordic end-users by 75% (2ms local vs 28ms from Frankfurt). Furthermore, hosting in Sweden ensures corporate data falls under Swedish Authority for Privacy Protection (IMY) oversight, avoiding the complex data interception frameworks active in central European jurisdictions.
Specifically, deploying on enterprise-grade sweden vs germany vps latency infrastructure provides engineering teams, growing Nordic enterprises, and global organizations with the compute power, regulatory sovereignty, and low-latency throughput necessary to run mission-critical applications. In a modern hosting landscape crowded with generic public cloud resellers, maintaining physical server residency within Stockholm ensures direct access to Scandinavia’s optical fiber backbone while eliminating the unpredictable performance penalties caused by noisy-neighbor hypervisor overcommitment.
📌 Master Chapter Directory
- 1. Physical Stockholm Infrastructure & Optical Peering
- 2. Hypervisor Virtualization Architecture & NVMe Storage
- 3. Empirical Performance Telemetry & Network Diagnostics
- 4. Data Sovereignty, IMY Privacy & Production Hardening
- 5. Architecture & Performance Evaluation Matrix
- 6. Hardware Resource Sizing & Transparent TCO Model
- 7. 7-Point Production Readiness & Deployment Checklist
- 8. Frequently Asked Questions & Architectural Answers
sweden vs germany vps latency: Physical Stockholm Infrastructure & Optical Peering
Consequently, aligning these configurations with your sweden vs germany vps latency environment ensures optimal uptime and throughput. Physical datacenter location serves as the definitive anchor for cloud performance and regulatory compliance. Contrasts the 20-35ms latency penalty of German/Dutch servers for Scandinavian users against the sub-5ms local response of Stockholm. When organizations deploy on an OnliveServer node in Stockholm, Sweden, their workloads reside within an interconnected Northern European junction engineered for high-availability enterprise services. Carrier-neutral facilities offer biometric access controls, continuous video telemetry, 24/7 on-site security personnel, and automated gaseous fire suppression systems compliant with EN 50600 European data center standards.
Netnod Internet Exchange Stockholm Connectivity
Consequently, aligning these configurations with your sweden vs germany vps latency environment ensures optimal uptime and throughput. Stockholm represents the telecommunications junction box of the entire Scandinavian peninsula. At the heart of this regional connectivity sits Netnod, one of Europe’s most established internet exchange points. Direct peering at Netnod enables traffic to bypass congested transit backbones and route directly to local Internet Service Providers, telecommunication networks, and corporate enterprise endpoints.
Furthermore, direct optical peering across Stockholm fabrics keeps domestic Swedish packet exchanges under 2ms for ultra-responsive API and database interactions.
Consequently, direct terrestrial and subsea links deliver predictable sub-10ms round-trip times to Oslo (6–8ms), Helsinki (7–9ms), and Copenhagen (8–11ms).
In addition, redundant upstream carrier transit via Telia (Arelion), Telenor, and Cogent guarantees automated failover during regional backbone maintenance.
In particular, for an inside look at enterprise colocation standards, power grids, and hardware security in the Swedish capital, see our Stockholm datacenter physical architecture.
Green Power Infrastructure & Environmental Resilience
Therefore, modern corporate IT mandates require demonstrable environmental accountability alongside raw compute power. Sweden maintains one of the cleanest electrical grids globally, drawing heavily from hydroelectric and wind generation. Datacenters in Stockholm leverage this fossil-free power infrastructure to achieve exceptionally low carbon footprints per compute cycle.
Moreover, onliveServer Stockholm facilities operate with an audited Power Usage Effectiveness (PUE) rating under 1.15. Server exhaust heat is channeled directly into Stockholm’s municipal district heating network to warm residential buildings, allowing international enterprises to fulfill strict ISO 14001 and European CSRD environmental sustainability criteria.
In fact, supported by dual 2N electrical feeds and automated N+1 diesel generator backup systems, our Stockholm datacenter guarantees 99.99% operational uptime without compromising environmental principles.
sweden vs germany vps latency: Hypervisor Virtualization Architecture & NVMe Storage
Similarly, virtualization technology dictates how reliably a cloud instance performs under sustained real-world load. Many ultra-cheap hosting providers rely on shared kernel container technologies like OpenVZ or shared LXC environments. While containers offer high tenant density and low provisioning overhead, they permit noisy neighbors to consume disproportionate memory pools and CPU cycles.
Dedicated Kernel Isolation with KVM Hypervisors
In contrast, OnliveServer implements pure Kernel-based Virtual Machine virtualization across all Stockholm cloud nodes. Network stack pacing and buffer management operate per the IETF BBR congestion control specification, maximizing TCP throughput across European long-haul routes.
- Meanwhile, Hardware-Level Virtualization: Each instance boots its own isolated, dedicated Linux or Windows kernel.
- Additionally, Strict Memory Reservation: Provisioned ECC DDR4/DDR5 RAM is fully committed with zero memory overcommit.
- As a result, Deterministic vCPU Slices: Dedicated thread scheduling eliminates noisy-neighbor CPU steal time.
- Specifically, Full Root Authority: Unrestricted freedom to load custom kernel modules (BBR, WireGuard, Docker namespaces).
- Furthermore, Shared Host Kernel: All tenants execute under the identical underlying host operating system kernel.
- Consequently, Severe Memory Contention: Host kernel aggressively terminates high-usage processes via the OOM-killer.
- In addition, Variable Performance: Neighboring tenants running crypto mining or traffic spikes degrade latency.
- In particular, Restricted Kernel Capabilities: Cannot modify sysctl network buffers or deploy private VPN tunnels.
Therefore, complete kernel isolation unlocks unrestricted root administrative control, enabling engineering teams to deploy WireGuard tunnels, load custom network modules, and configure nested Docker containers without hypervisor limitations.
Enterprise NVMe PCIe 4.0 Storage & IOPS Ceilings
Moreover, disk input-output performance frequently represents the primary bottleneck for dynamic database applications. Traditional SATA solid-state drives cap throughput around 550 megabytes per second and struggle with high queue depths. OnliveServer equips its Swedish hypervisors with pure enterprise PCIe 4.0 NVMe storage configured in resilient hardware RAID 10 arrays.
In fact, sustained random write throughput per provisioned virtual slice
Similarly, direct PCIe bus communication without SATA controller bottlenecks
Meanwhile, dual redundancy with hot-swappable drives ensuring zero downtime
PCIe 4.0 NVMe architecture yields sustained random read and write speeds exceeding 45,000 IOPS per virtual volume. For transactional databases like PostgreSQL, MySQL InnoDB, and high-throughput Redis caching layers, this storage performance eliminates I/O wait times and prevents database locks during heavy concurrent traffic surges.
Empirical Performance Telemetry & Network Diagnostics
Additionally, transparent telemetry separates credible hosting providers from marketing aggregators. To verify the performance advantages of our Stockholm datacenter for stockholm vs frankfurt vs amsterdam vps: regional routing comparison, administrators can execute standardized diagnostic runbooks directly from their server terminals.
Diagnostic 1: Verifying BGP Routing & Nordic Round-Trip Times
As a result, using modern command-line network diagnostic tools like mtr, administrators can inspect packet transit paths and hop-by-hop latency from Stockholm across major Scandinavian communication hubs:
As evidenced by the telemetry above, packets originating from our Stockholm datacenter reach Oslo, Helsinki, and Copenhagen in less than 10 milliseconds over direct terrestrial dark fiber, with 0.0% packet drop and under 0.4ms jitter across 100 consecutive ICMP probes.
Diagnostic 2: Benchmarking NVMe Random I/O with FIO
To verify that your storage volume delivers true enterprise NVMe throughput without hypervisor disk throttling, run this standardized flexible I/O tester benchmark directly from your shell:
These empirical metrics demonstrate that OnliveServer KVM nodes provide dedicated I/O queues capable of supporting heavy transactional workloads. Average latency remains under 200 microseconds even during intensive mixed read-write operations, ensuring that database locks and uncommitted transactions clear rapidly.
Data Sovereignty, IMY Privacy & Production Hardening
Hosting customer personal data involves substantial legal liabilities. Within Sweden, data protection standards are actively monitored and enforced by Integritetsskyddsmyndigheten (IMY), the Swedish Authority for Privacy Protection. While IMY operates under the unified framework of the European GDPR, Swedish regulatory interpretations place immense emphasis on verifiable data residency, technical encryption standards, and third-party access restrictions.
Navigating the US CLOUD Act & Post-Schrems II Precedents
Following the landmark Schrems II European Court of Justice ruling, organizations storing sensitive customer records on US-owned hyperscale clouds face legal exposure. Under the United States CLOUD Act, American authorities can compel US-headquartered cloud providers to surrender customer data stored on foreign servers without local court approval. This creates direct compliance friction with European privacy mandates.
Deploying on an independent Swedish virtual server ensures data resides entirely under European Union and Swedish sovereign jurisdiction. OnliveServer operates under European corporate governance with zero parent-company obligations to foreign surveillance subpoenas, executing binding Data Processing Agreements (DPAs) that guarantee physical partition residency in Stockholm.
To verify regional network round-trip advantages across Sweden, Norway, Denmark, and Finland, check our Nordic-specific latency benchmarks.
Swedish Public Access & Secrecy Act (OSL) Protections
In addition to standard GDPR requirements, Sweden maintains the Offentlighets- och sekretesslagen, known as the Public Access to Information and Secrecy Act. This statute governs how sensitive commercial information, medical data, and technical trade secrets must be insulated from administrative disclosure. For healthcare platforms, fintech startups, and professional service agencies, hosting under Swedish jurisdiction establishes a legally recognized privacy shelter.
Enforce AES-256 bit encryption at rest on all NVMe partitions to prevent offline block extraction.
Disable outdated TLS 1.0/1.1 protocols and restrict cipher suites to ChaCha20 and AES-GCM.
Disable SSH root password logins and enforce cryptographic public-key authentication with MFA.
Automate incremental snapshots to secondary European cold storage with immutable retention locks.
Combining statutory Swedish secrecy protections with disciplined system-level hardening ensures that production environments remain legally sheltered and technically impervious to unauthorized administrative access.
Architecture & Performance Evaluation Matrix
When evaluating cloud infrastructure for stockholm vs frankfurt vs amsterdam vps: regional routing comparison, comparing technical dimensions directly helps clarify architectural trade-offs. The comparative matrix below highlights the operational differences between deploying locally on an OnliveServer Stockholm node versus generic central European hosting:
| Architecture Dimension | OnliveServer Stockholm VPS | Generic Frankfurt / Amsterdam Cloud |
|---|---|---|
| Nordic Latency (SE, NO, FI) | Sub-10ms Direct Netnod IX Peering | 28ms – 45ms Continental Loop |
| Hypervisor Architecture | Pure KVM Virtualization (Dedicated Kernels) | Variable (Containers or Overcommitted KVM) |
| Storage Media & Bus | Enterprise PCIe 4.0 NVMe RAID 10 | SATA SSDs or Shared Network Ceph SAN |
| Data Sovereignty Jurisdiction | Swedish Authority for Privacy Protection (IMY) | German / Dutch National Privacy Regulators |
| US CLOUD Act Exposure | Immune (Independent European Operations) | Exposed if US-Owned Hyperscaler Region |
| Environmental Energy Grid | 100% Fossil-Free Hydro & Wind (PUE < 1.15) | Continental Mixed Grid (PUE 1.35 – 1.50) |
| Network Egress Surcharges | Zero Egress Surcharges (Unmetered 1Gbps) | $0.08 – $0.12 per Gigabyte Outbound |
Hardware Resource Sizing & Transparent TCO Model
Calculating the true total cost of ownership for cloud infrastructure extends far beyond the base monthly compute invoice. To discover how local IX fabric integration eliminates the need for expensive continental transit routes, review the Netnod peering advantage. In contrast, OnliveServer structures its Sweden VPS tiers around transparent resource allocations with generous bandwidth allowances.
Stockholm VPS Resource Sizing & Pricing Tiers
To assist engineering managers in matching workloads to hardware profiles, the table below outlines our primary Sweden VPS configurations, hardware baselines, and recommended operational use cases:
| Plan Tier | Compute Hardware | Storage & Port | Base Price | Ideal Workload |
|---|---|---|---|---|
| Sweden Starter | 1 vCPU / 1 GB RAM | 25 GB NVMe / 1Gbps Unmetered | $8 / mo | DNS, WireGuard VPN, microservices, staging environments |
| Sweden Standard | 2 vCPU / 2 GB RAM | 50 GB NVMe / 1Gbps Unmetered | $16 / mo | WordPress corporate websites, dynamic PHP web applications |
| Sweden Pro | 4 vCPU / 4 GB RAM | 100 GB NVMe / 1Gbps Unmetered | $32 / mo | High-concurrency WooCommerce stores, PostgreSQL backends |
| Sweden Business | 4 vCPU / 8 GB RAM | 150 GB NVMe / 1Gbps Unmetered | $55 / mo | Multi-tenant SaaS platforms, Docker microservice clusters |
| Sweden Enterprise | 8 vCPU / 16 GB RAM | 250 GB NVMe / 1Gbps Unmetered | $89 / mo | Enterprise ERP portals, gaming servers, high-volume APIs |
| Sweden High-Memory | 8 vCPU / 32 GB RAM | 400 GB NVMe / 1Gbps Unmetered | $139 / mo | In-memory data grids, Redis clusters, elasticsearch indexes |
Eliminating Egress Fees & Unpredictable Metering
On major proprietary public clouds, egress network bandwidth often costs between $0.08 and $0.12 per gigabyte transferred out. For media streaming platforms, backup transfers, or high-volume API gateways delivering 10 terabytes monthly, outbound bandwidth fees alone can exceed $1,000. In contrast, OnliveServer includes unmetered 1Gbps network connectivity on premium Swedish transit routes.
1Gbps unmetered network connection included with every plan, eliminating surprise $1,000+ egress bandwidth invoices.
Predictable flat billing in USD, EUR, or SEK insulates infrastructure expenditure from foreign exchange volatility.
Support for global credit cards, PayPal, bank wire invoicing, and privacy-focused cryptocurrencies (BTC, ETH, USDT).
Zero egress fees and currency-stable billing provide engineering executives with financial predictability, preventing cloud invoice inflation as monthly usage scales.
7-Point Production Readiness & Deployment Checklist
Before signing a hosting contract or transferring production data to a new server for stockholm vs frankfurt vs amsterdam vps: regional routing comparison, engineering teams should evaluate prospective hosting providers against this systematic 7-point technical verification checklist:
Confirm that the hosting provider operates actual physical bare-metal hardware inside a certified Stockholm facility rather than white-labeling third-party transit.
Verify true KVM virtualization with dedicated kernel isolation rather than shared container environments that permit noisy-neighbor contention.
Ensure the storage architecture utilizes PCIe 4.0 NVMe in hardware RAID 10, delivering over 45,000 IOPS and sub-200 microsecond latency.
Check traceroutes to confirm domestic traffic exchanges at Netnod Stockholm, guaranteeing sub-10ms round-trip times across Scandinavia.
Confirm unrestricted SSH and root authority, enabling custom kernel parameters, proprietary security baselines, and nested container virtualization.
Ensure clean IP reputations, customizable reverse DNS records for corporate mail servers, and routed native IPv6 subnets.
Secure a GDPR-compliant DPA ensuring data residency remains inside Sweden, protected from extraterritorial US CLOUD Act exposure.
Systematically auditing prospective hosting partners against these criteria ensures your enterprise infrastructure achieves optimal balance across raw compute horsepower, network velocity, and legal compliance.
Frequently Asked Questions
Core Technical Specifications
When should a business choose a Sweden VPS instead of a Frankfurt, Germany VPS?
Choose a Sweden VPS if your primary audience, corporate offices, or compliance requirements reside in Sweden, Norway, Denmark, Finland, or the Baltic states. Local hosting saves 20ms to 35ms of latency compared to Frankfurt.
How does Frankfurt cloud hosting introduce network latency for Scandinavian users?
Traffic from Stockholm to Frankfurt must traverse trans-European terrestrial fiber routes across Denmark and northern Germany, adding approximately 25ms to 35ms of round-trip transit time and multiple routing hops.
Are there legal and regulatory differences between hosting in Sweden versus Germany?
While both nations adhere to EU GDPR, Sweden offers stronger constitutional protections for telecommunications privacy and strict source confidentiality under the Freedom of the Press Act, contrasting with Germany’s complex state data-retention frameworks.
Does hosting in Sweden improve SEO rankings for Scandinavian localized search queries?
Yes. Search engine crawlers consider server geographic location and fast local TTFB as localized relevance signals for Nordic search queries, giving domestic sites an edge in localized SERPs.
Deployment & Operational Inquiries
Can a company deploy hybrid multi-region architectures between Sweden and Germany?
Yes. Many enterprise clients run primary transactional workloads in Stockholm for Scandinavian customers while maintaining replicated standby nodes in Frankfurt for central European failover.
What latency difference is observed for database replication between Stockholm and Frankfurt?
Synchronous database replication across 30ms latency links can introduce noticeable write latency; asynchronous master-slave replication or active-passive DR topologies are recommended when spanning Sweden and Germany.
How do bandwidth and egress costs compare between Swedish and German datacenters?
German hyperscaler facilities often charge heavy egress transfer fees. OnliveServer Stockholm hosting provides unmetered 1 Gbps bandwidth, delivering greater cost predictability for data-heavy applications.
Deploy Your High-Performance Stockholm vs Frankfurt vs Amsterdam VPS: Regional Routing Comparison Today
Experience enterprise-grade KVM hardware isolation, ultra-fast NVMe storage, and 1Gbps unmetered bandwidth stationed directly inside a certified Stockholm datacenter starting from $8/mo.
Explore Sweden VPS Plans & Pricing →