

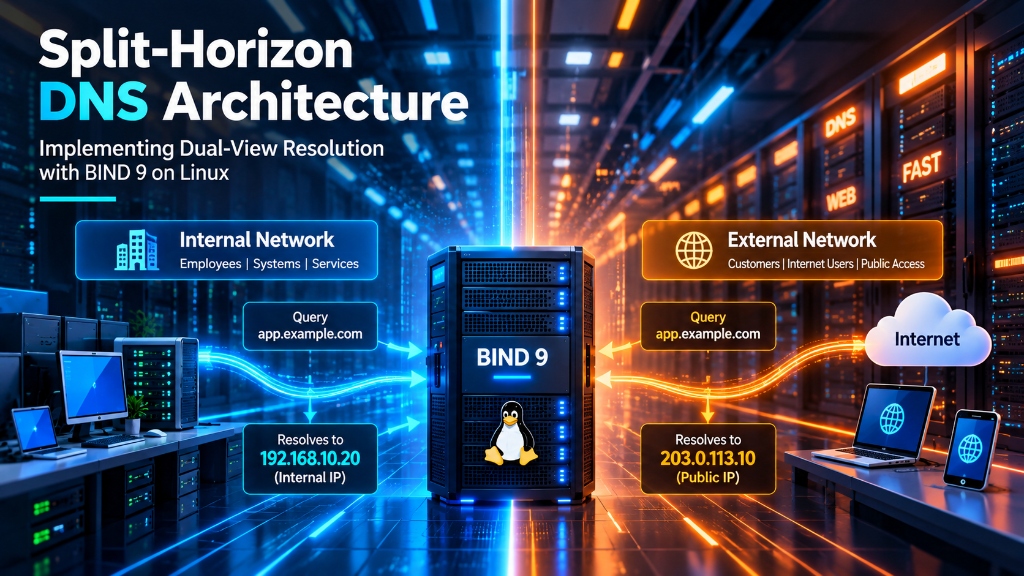
⚡ Split-Horizon DNS Architecture: Executive Summary
- Dual-View Network Isolation: A Split-Horizon DNS architecture serves different DNS responses based on the requester’s IP, keeping internal traffic safely contained within the private VPC.
- Eliminate Hairpin NAT: Instead of routing internal server-to-server queries through a public gateway, microservices resolve directly to private IPs, slashing latency and saving bandwidth.
- BIND 9 View Configurations: With powerful Access Control Lists (ACLs) in BIND 9, you can easily segment public queries from internal queries under a single, unified domain namespace.
- Enterprise VPS Performance: By hosting your nameservers on reliable UK VPS solutions, you guarantee sub-millisecond DNS resolutions for critical infrastructure.
Table of Contents
- 1. Introduction: Solving the Internal/External DNS Dichotomy
- 2. Architecture Topology: Public Edge vs Private VPC Networks
- 3. BIND 9 View-Based Configuration: ACLs and Zone Separation
- 4. Internal vs External Zone File Definitions
- 5. Unbound as a Caching Resolver for Split-Horizon DNS
- 6. Security Implications: Preventing DNS Data Leaks
- 7. Conclusion & FAQ
1. Introduction: Solving the Internal/External DNS Dichotomy
Modern enterprise infrastructures, web applications, and databases exist in hybrid environments spanning public cloud interfaces and isolated Virtual Private Clouds (VPCs). When it comes to routing internal service traffic, an effective Split-Horizon DNS Architecture solves a crucial challenge. Without it, you are forced to choose between unnecessary external routing or managing disparate hostnames.
The Split-Horizon DNS Architecture Advantage
Consider an API service hosted at api.enterprise.com. Without Split-Horizon DNS (also known as Split-Brain DNS), administrators must either point the A record to a public IP—causing “hairpin NAT” latency penalties—or create separate internal domains like api-internal.corp.lan. This fractures configuration logic and complicates SSL/TLS validation.
By implementing a Split-Horizon DNS architecture, you maintain a single unified domain namespace. The DNS server dynamically segments resolution based on the client IP address. Public internet visitors resolve endpoints to external firewalls, while internal worker nodes resolve the identical hostname directly to private 10.x.x.x LAN interfaces.
2. Architecture Topology: Public Edge vs Private VPC Networks
In a standard split-horizon setup, the DNS server evaluates incoming queries against configured Access Control Lists (ACLs) before serving the answer.
Deploying this dual-view topology on robust hardware, such as a managed dedicated server, allows you to establish secure internal communication channels with minimal latency.
3. BIND 9 View-Based Configuration: ACLs and Zone Separation
BIND 9 (Berkeley Internet Name Domain) provides native support for Split-Horizon DNS architecture via the view statement. The configuration involves setting up distinct ACLs for internal trusted networks.
Configure /etc/bind/named.conf.local on your authoritative nameserver:
4. Internal vs External Zone File Definitions
Inside the internal zone file, service endpoints resolve to private RFC 1918 addresses.
Conversely, in the external zone file, sensitive internal endpoints like db and staging are completely omitted. Only public-facing edge services are exposed, securing your network against public DNS enumeration.
5. Unbound as a Caching Resolver for Split-Horizon DNS
While BIND 9 serves as the authoritative source, deploying Unbound as a caching resolver on worker nodes accelerates lookup times. Unbound caches responses in RAM, allowing microservices to perform lookups in under 0.2 milliseconds.
By leveraging secure domain registration and DNS routing, your caching setup ensures highly available and rapid internal communications.
6. Security Implications: Preventing DNS Data Leaks
A proper Split-Horizon DNS architecture necessitates strict defensive measures:
- Disable Public Recursion: External views must have
recursion no;to prevent DNS Amplification DDoS attacks. - Strict ACL Ordering: BIND evaluates views sequentially. Always place the most restrictive internal view first.
- Isolate DNS Caches: Never allow internal and external queries to share the same resolver cache to avoid cache poisoning attacks.
7. Conclusion & FAQ
Implementing a Split-Horizon DNS architecture with BIND 9 allows organizations to maintain high-performance internal routing while securing sensitive infrastructure from the public internet. This configuration ensures faster database connections, lowers external bandwidth usage, and provides a centralized naming schema.
Frequently Asked Questions
Q1: What is Split-Horizon DNS architecture?
It is a DNS configuration method that returns different IP addresses for the same hostname based on the source network of the DNS query. Internal users get local IPs, and external users get public IPs.
Q2: Why should I disable recursion on the external view?
Leaving recursion enabled on public-facing DNS servers opens them up to amplification attacks, where attackers spoof source IPs and flood a victim with large DNS responses.
Q3: Can Split-Horizon DNS be used with Kubernetes?
Yes, in Kubernetes, CoreDNS is configured to rewrite external domain queries to internal Ingress Controller IPs using the rewrite and hosts plugins, effectively achieving split-horizon resolution.

